At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in USDC bridged from Ethereum—initiated a series of commands that began systematically draining card-balance accounts held by users of Avici, a Solana-based neobank. By the time the event concluded, 1,685 users had seen their balances siphoned, totaling a loss of $500,859.22. This incident, while relatively contained, exposed the fragile architecture underlying the booming market for self-custodial crypto debit cards.
The mechanism behind the loss was not a compromise of individual user private keys, nor was it a breach of the users’ personal wallets. Instead, the vulnerability resided within the smart contract layer that serves as the bridge between on-chain collateral and traditional payment networks. Avici’s terms of service, last updated on June 23, 2025, claimed that "Avici and Issuer will not, in any circumstance, be holding custody of your Collateral." While legally accurate in the traditional sense, the clause provided no protection against a technical exploit in the shared contract infrastructure.
The Anatomy of the Solana Card Exploit
The breach involved a specific vulnerability in a Solana card contract managed by Rain, the infrastructure provider that powers the majority of the self-custodial card market. The attacker’s wallet, identified by the address FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, executed 21,405 transactions within a window of approximately 150 minutes, with nearly 17,500 of those attempts succeeding.
Each successful transaction followed a precise, three-step sequence: a SubmitSignatures call, an AddCollateralAdmin instruction, and a final WithdrawCollateralAsset command. The flaw allowed the attacker to use a single signature to satisfy a two-signature verification requirement by manipulating message offsets within the Ed25519 signature-verification instruction. This granted the attacker administrative control over more than 1,000 individual user collateral accounts.
The exploit targeted three distinct Rain program IDs. By 19:18:37 UTC, fifteen seconds before the attacker ceased activity, Rain successfully deployed a patch to the most heavily impacted program. The remaining affected programs were patched shortly thereafter. On September 5, 2026, Rain transitioned the upgrade authority for these contracts to a Squads multisig vault, a significant security improvement over the single, plain keypair previously used.
Financial Repercussions and Market Impact
While the technological failure was significant, the immediate financial fallout for users was mitigated by the rapid intervention of the program managers. Avici confirmed that all affected users were fully refunded, with the company adding a 10% premium on top of the losses to restore confidence. Tria, another program affected by the same vulnerability, reported losses of $431,945 across 636 accounts and likewise covered the full amount plus a 10% bonus.
However, the market reaction was swift. The $AVICI token plummeted approximately 49% within 24 hours of the news. The incident also forced a broader re-evaluation of the "non-custodial" marketing narrative. While users held the keys to their primary wallets, the funds deposited into the card-linked collateral accounts were subject to the security of the shared Rain infrastructure.
The Infrastructure Concentration Risk
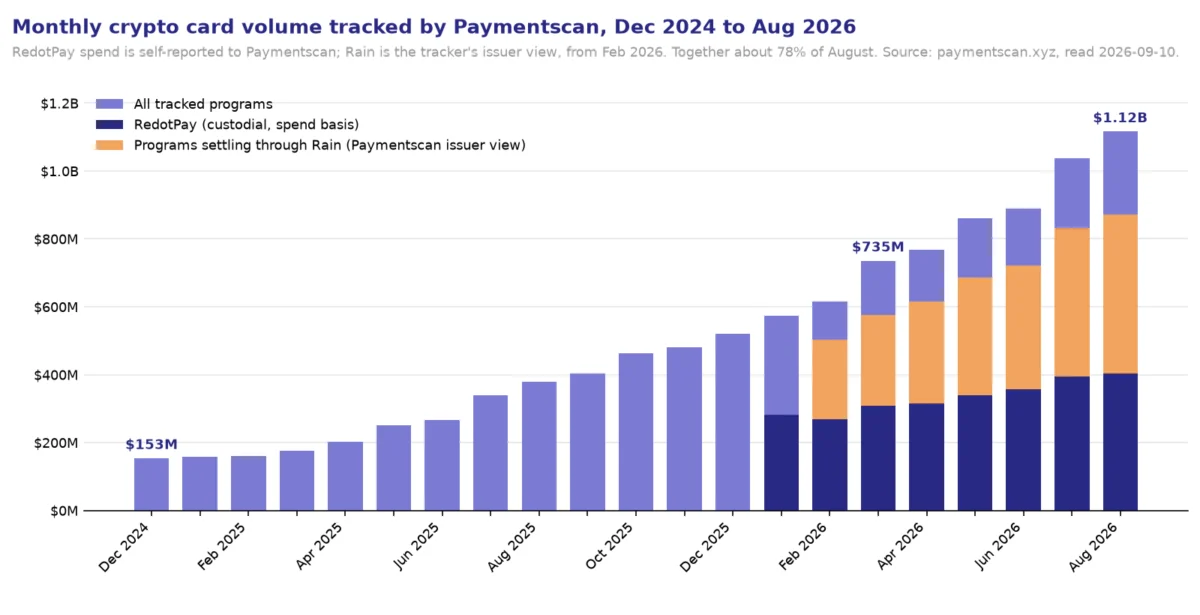
Data from Paymentscan indicates that the crypto card sector has seen explosive growth, with monthly volume reaching $1.116 billion in August 2026, spanning 11 million transactions and 287,640 active addresses. Yet, this growth masks a significant concentration risk. Rain-settled programs accounted for roughly 42% of the total monthly volume, and when combined with RedotPay, two entities represent nearly 78% of the entire tracked crypto card market.

This concentration extends to the issuing layer. Seven major programs—KAST, Avici, Ether.fi Cash, Plasma One, Solayer, Payy, and Tria—name "Third National" as their card issuer. Investigations reveal that Third National is not a traditional bank, but rather a Puerto Rico-based money transmitter and an affiliate of Rain. This structure means that much of the market’s stability rests on a single group’s compliance, operational security, and capital liquidity.
A Spectrum of Custody Models
The August 28 incident highlights the necessity of distinguishing between the five primary custody models currently operating in the crypto card space.
- Sold to the Operator: Programs like KAST have moved toward a model where user deposits are treated as a sale of assets, converting the user’s crypto into a USD-denominated debt claim. In this model, if the provider faces bankruptcy, users rank as general creditors.
- Custodial Nominee: Platforms like RedotPay and Revolut act as custodians, where the company holds legal title to the assets on behalf of the user. This is standard in traditional fintech but introduces third-party risk.
- Fiat-Converted: Exchange cards, such as those from Crypto.com or Kraken, often hold only fiat currency on the card account itself. The crypto is sold only at the moment of authorization, removing the need for crypto-asset custody on the card network.
- Program-Pool Contracts: This is the category containing Avici and Tria. While users ostensibly own their collateral, the assets are held in smart contracts where the program manager holds the upgrade authority and administrative keys, creating a single point of failure.
- Self-Custodial Vaults: Programs like Gnosis Pay and Ether.fi Cash represent the highest tier of security, where funds are held in smart accounts (such as Gnosis Safes) that the operator cannot unilaterally move. These systems often utilize modules to manage spend limits, providing a more robust security posture.
Regulatory and Operational Hurdles
The crypto card industry faces mounting pressure from global regulators. The European Union’s Anti-Money Laundering Regulation (EU 2024/1624), set to take full effect in July 2027, will effectively prohibit anonymous crypto-asset accounts and limit the usage of non-reloadable, non-KYC cards.
The industry’s reliance on "no-KYC" marketing has also drawn scrutiny. Recent audits of eleven "no-KYC" cards revealed that only one transparently named its issuer. Many of these services utilize a regulatory loophole involving "Know Your Business" (KYB) verification, where a company clears institutional hurdles and subsequently issues cards to individuals without secondary identity checks.
The mortality rate for these programs remains high. When infrastructure providers like Paytend Europe UAB face regulatory intervention, as seen in March 2026, the brands that rely on them are often left helpless. In that instance, the provider’s license revocation resulted in a total freeze of funds, with the brands themselves unable to process refunds.
Lessons for the Future
The August 28 incident serves as a critical case study in the gap between the marketing of "self-custody" and the technical reality of smart contract implementation. "Self-custody" is frequently used as a shorthand for security, but the term does not inherently account for who authored the code, whether the deployed version underwent a comprehensive audit, or who retains the power to upgrade that code.
As the industry matures, stakeholders are increasingly calling for greater transparency. The divide between Ether.fi, which uses public smart contracts with clear recovery signers, and programs that operate behind opaque, login-gated documentation, is widening. For the average cardholder, the primary lesson is that while the promise of non-custodial finance is transformative, the infrastructure currently powering these cards remains experimental.
Ultimately, the decision to refund users in full, while commendable, was a business decision made by a venture-backed company to preserve its reputation. As the sector moves toward an annualized run rate exceeding $20 billion, the market will likely demand more than just corporate goodwill; it will require the adoption of standardized, transparent, and immutable security protocols that do not rely on a single administrative key to protect hundreds of millions of dollars in user funds. Whether the current ecosystem of 160+ stablecoin-linked card programs can pivot toward this standard before the next major vulnerability is tested remains the defining challenge for the remainder of the decade.