At 16:49:48 UTC on Friday, August 28, 2026, a Solana wallet—funded just three hours prior with 1.79 SOL derived from $190 in USDC bridged from the Ethereum network—initiated a systematic drainage of card-balance accounts associated with Avici, a prominent Solana-based neobank. While Avici’s terms of service, last updated in June 2025, explicitly stated that neither the platform nor the issuer held custody of user collateral, the technical reality of the infrastructure proved far more vulnerable than the legal disclaimers suggested. Within hours, the incident confirmed the fears of many security researchers: even in "non-custodial" arrangements, the code managing the funds often remains under the unilateral control of the program manager.
By the time the breach was contained, Avici’s internal reconciliation revealed that 1,685 users had lost a collective $500,859.22. The vulnerability resided not in the users’ private wallets, but in a shared "Solana card contract" utilized by Avici and several other programs within the ecosystem. The infrastructure, provided by the card-issuing firm Rain, acted as the backbone for a significant portion of the self-custodial card market. While Avici and the secondary program Tria, which was also impacted, managed to cover all losses with an additional 10% premium, the incident exposed systemic risks that extend far beyond a single bank.
A Chronology of the August 28 Exploit
The breach was a masterclass in precision and speed. The attacker’s wallet, identified as 0xFVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj, remained dormant for 189 minutes after its initial funding. Once the attack commenced, it executed roughly 21,405 transactions, of which 17,500 were successful, over a window of approximately 150 minutes. The mechanism involved a signature-verification flaw in the native Ed25519 instructions within Rain’s Solana program. By manipulating signature and key offsets, the attacker bypassed the requirement for two-party authorization, effectively granting themselves administrative access to individual user collateral accounts.
The attacker moved rapidly to launder the stolen assets. Between 19:03 and 19:49 UTC, the funds were bridged back to Ethereum and channeled through Tornado Cash in a standard laddered deposit pattern. By the time Rain patched the vulnerability at 19:18 UTC for the most severely affected program, the majority of the liquid capital had already been obfuscated. Rain later transitioned its upgrade authority to a secure Squads multisig vault on September 5, a critical security upgrade that should have been in place long before the breach occurred.
The Landscape of Crypto Card Custody
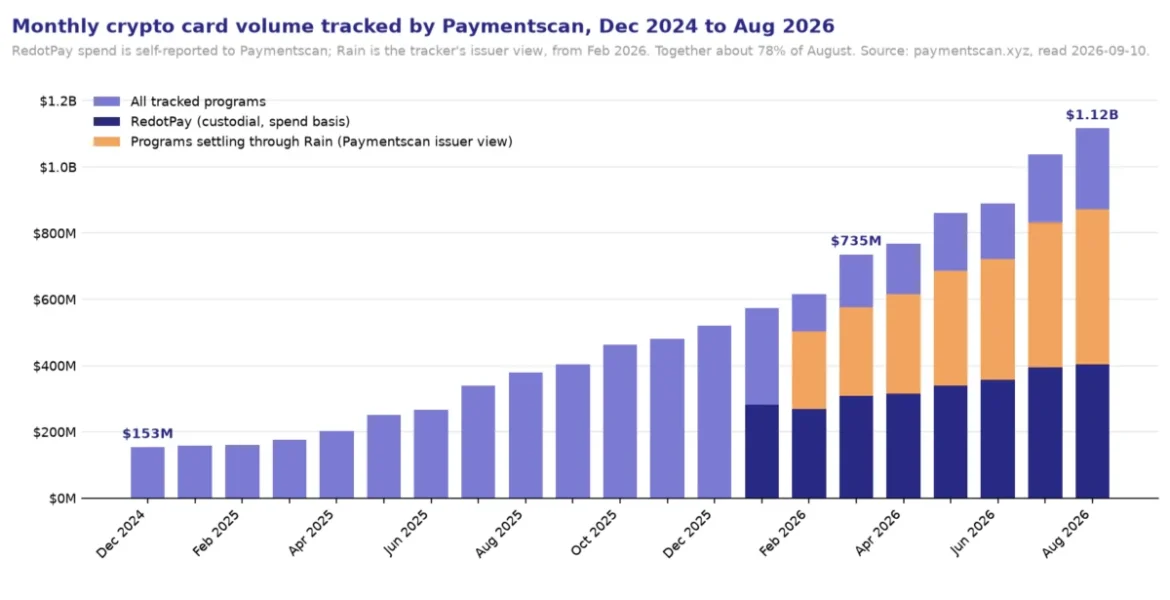
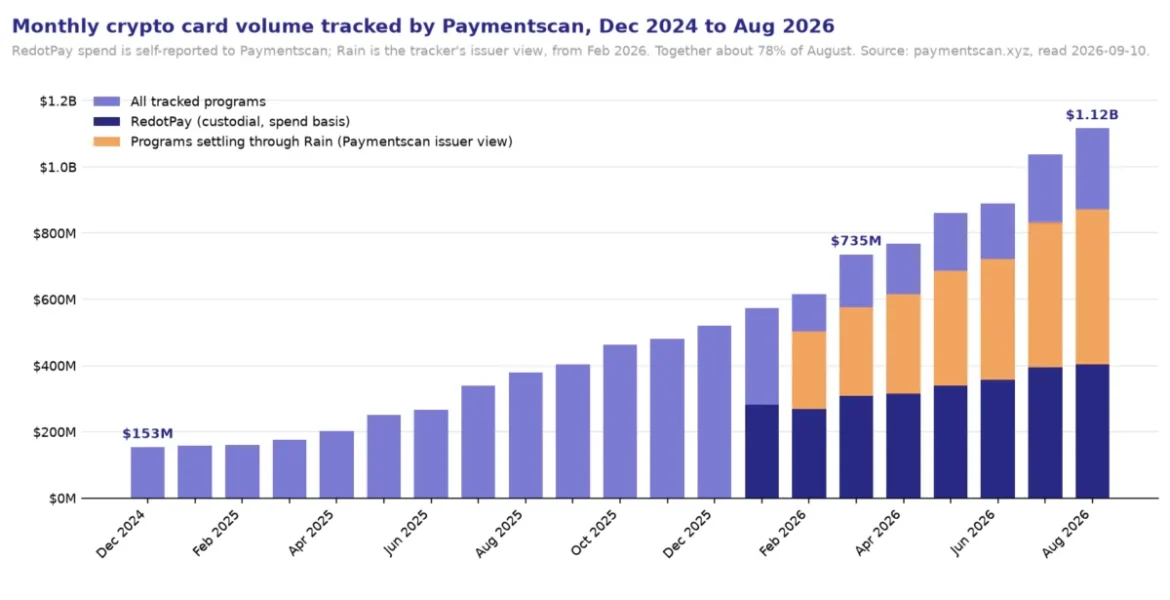
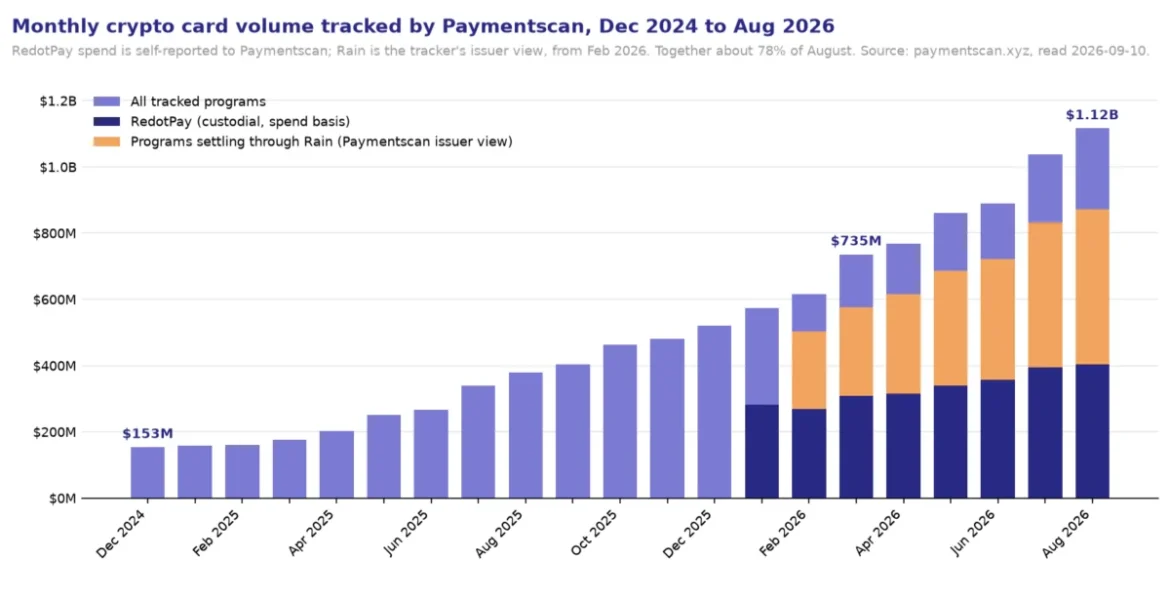
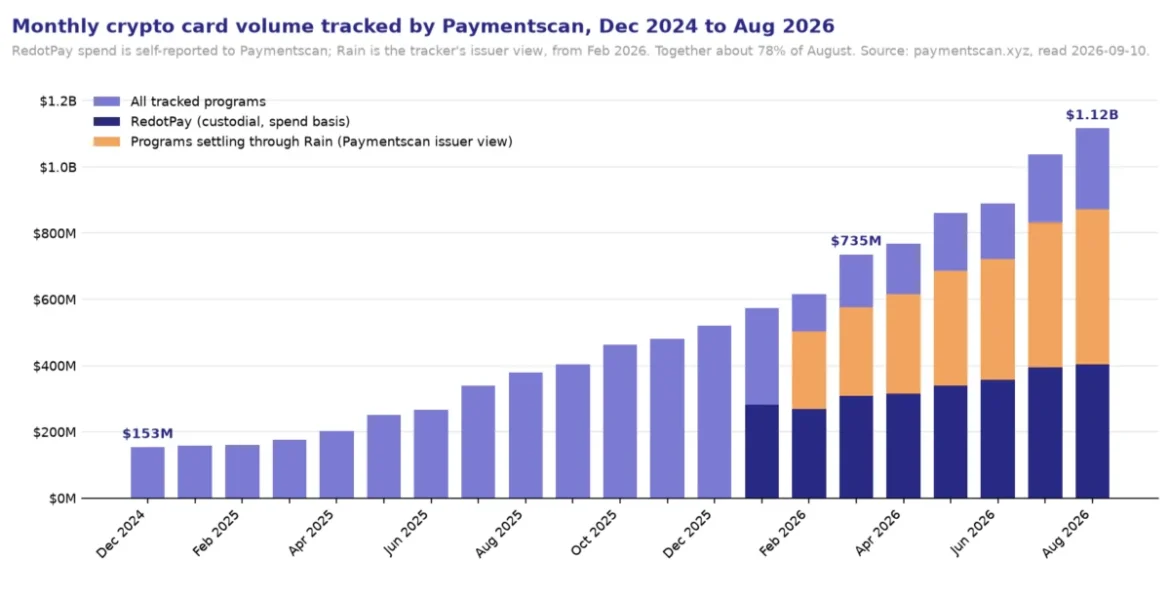
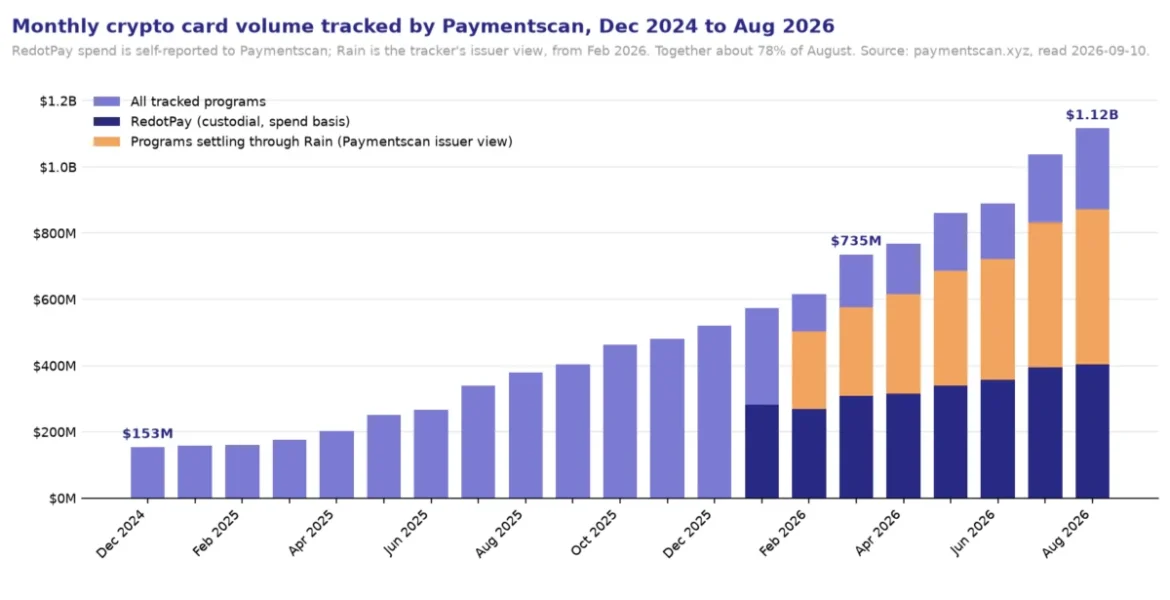
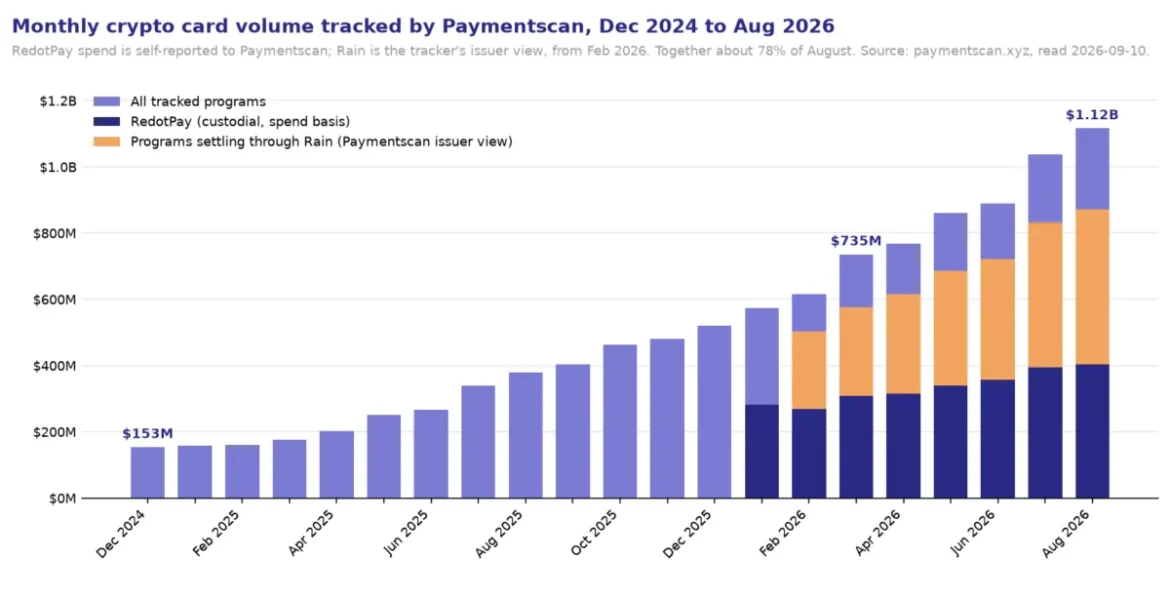
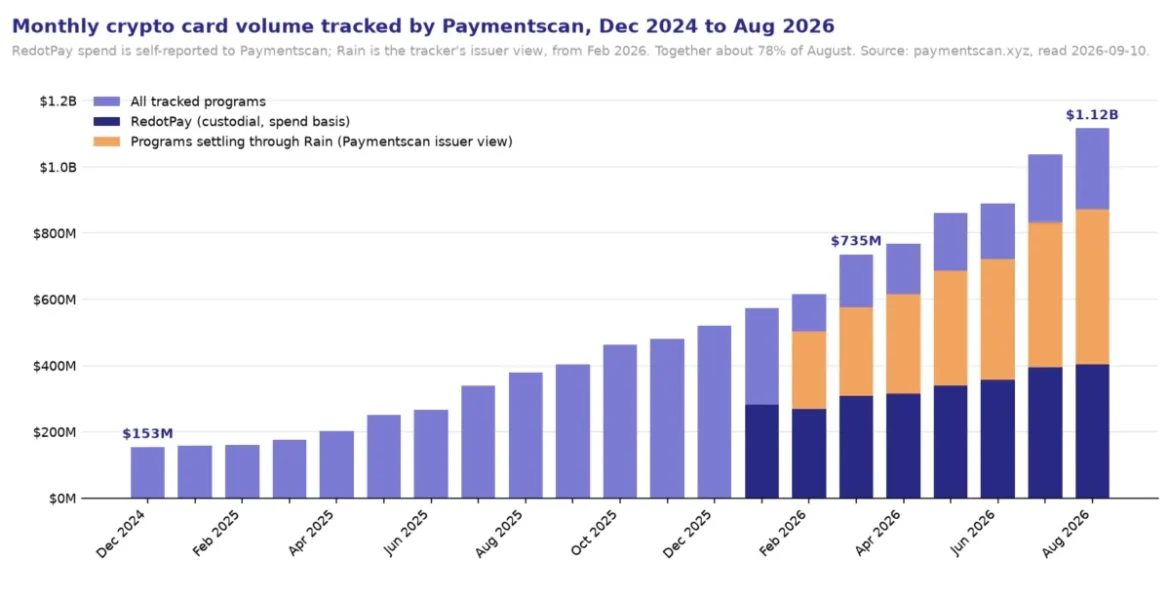
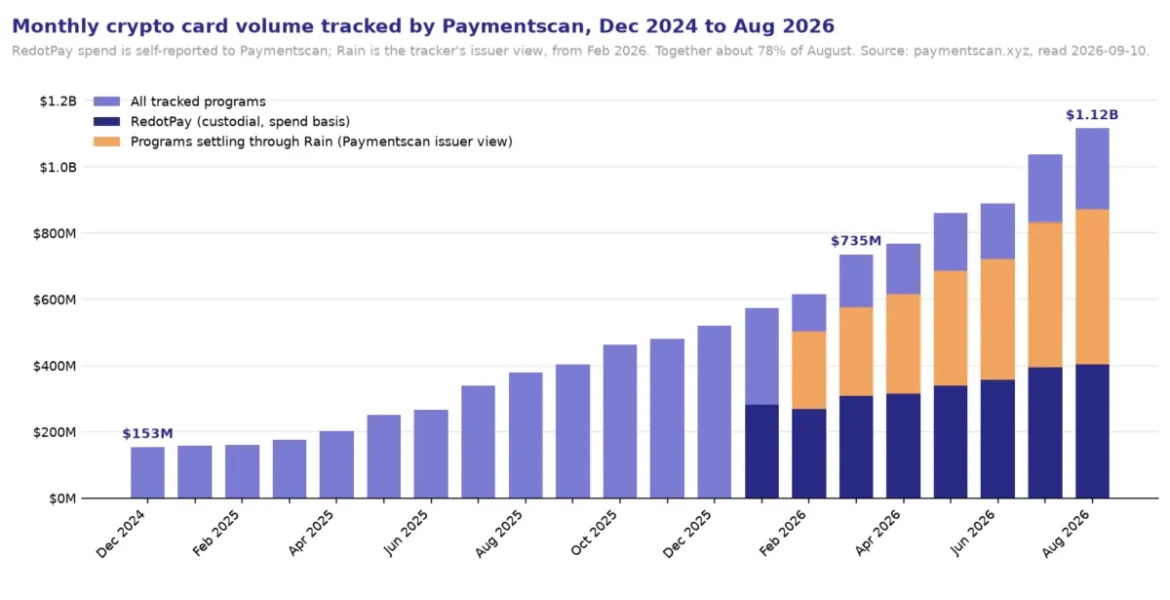
To understand the scope of this failure, one must categorize the five distinct models currently dominating the $1.1 billion-per-month crypto card industry. As of September 2026, Paymentscan data indicates that volume has surged from $153 million in late 2024 to over $1.1 billion, with 287,640 active addresses engaged in monthly transactions.
- Sale to Operator: Models like KAST treat user deposits as a sale of assets, converting crypto into a USD-denominated debt claim. In this model, the user is an unsecured creditor, and their claim is often capped, leaving them with little recourse in the event of bankruptcy.
- Custodial Nominee: Platforms like RedotPay and Revolut hold assets in a "nominee" capacity. While they claim to hold legal title on behalf of the user, the funds are legally commingled within the platform’s broader corporate treasury or omnibus accounts.
- Fiat Conversion: Exchange-based cards from providers like Crypto.com or Kraken do not hold crypto on the card at all. Instead, they facilitate a just-in-time conversion to fiat currency, which is held by a licensed banking partner. In the EU, these funds are subject to "safeguarding" requirements, which offer a statutory layer of protection against insolvency.
- Program-Managed Smart Contracts: This is the category occupied by Avici and Tria. Here, users fund a smart contract, but the program manager (Rain) retains the authority to upgrade that contract. The failure of August 28 proved that this "non-custodial" label is effectively a marketing term rather than a technical guarantee of user control.
- Vault-Based Self-Custody: The most secure model, utilized by Gnosis Pay and Ether.fi Cash, involves smart contracts where the user retains exclusive control via signing keys or hardware-isolated enclaves. In these models, the operator cannot move the funds, as the smart contract logic is immutable or governed by user-defined roles.
The Third National Problem
A recurring theme in the 2026 infrastructure audit is the reliance on "Third National." Seven major programs—KAST, Avici, Ether.fi, Plasma One, Solayer, Payy, and Tria—all identify Third National as their card issuer. However, Third National is not a bank. It is a subsidiary of Signify Holdings (Rain), licensed as a money transmitter in Puerto Rico.
This concentration creates a single point of failure. When Visa or the issuer decides to terminate a program, as seen previously with the closure of Bit.Store following the revocation of Paytend’s license, the brand that the customer interacts with has no power to intervene. The reliance on borrowed stablecoins to facilitate settlement adds another layer of financial complexity, as the card programs are essentially operating as high-velocity credit lines financed by capital partners.

The No-KYC Illusion
The "no-KYC" (Know Your Customer) card sector has been particularly volatile. A recent price list circulated in the community highlighted the high costs and hidden fees associated with these cards. However, the true risk lies in the regulatory arbitrage. As the EU’s Anti-Money Laundering Regulation (2024/1624) approaches full implementation in July 2027, the window for anonymous prepaid cards is rapidly closing.
Articles 19 and 79 of the new regulation will effectively prohibit anonymous crypto-asset accounts and bar EU acquirers from processing transactions from third-country anonymous cards. The implication is clear: the current generation of no-KYC cards, which rely on the gap between business-level verification and user-level anonymity, will likely face severe operational headwinds. The sudden shutdowns of Bit.Store and the instability of programs like SolCard are early warnings of a market that is increasingly incompatible with global financial standards.
Infrastructure Failures and Market Consolidation
The August exploit was the most visible failure, but it was not the only one. The industry saw a wave of quiet collapses in 2026. Kulipa, which raised $6.2 million in venture funding, halted operations in July, effectively ending the card programs for Ready and Solflare. Similarly, the acquisition of Cypher by Nium and the subsequent shutdown of Cypher’s platform terminated the Moonwell card.
Even Gnosis Pay, the gold standard for self-custodial card design, announced the winding down of its consumer-facing interface in September. While the underlying technology remains viable as a white-label solution, the consumer product failed to reach the scale necessary to remain independent.
Strategic Analysis: Implications for Users
The overarching lesson of the 2026 crypto card landscape is that the terminology used in legal agreements is rarely indicative of the technical risk. A card described as "non-custodial" may still be subject to the whims of an administrator who holds the upgrade keys.
For users, the priority must shift from trusting marketing materials to verifying technical architecture. Essential due diligence now includes:
- Verifying the Issuer: If the issuer is a money transmitter rather than a regulated bank, the program is inherently more fragile.
- Audit Transparency: Does the company publish the addresses of its smart contracts? If the documentation is behind a login or entirely absent, the user is operating on faith.
- Insolvency Clauses: Does the contract explicitly state how funds are handled if the company fails? If it does not, the user should assume the funds are at risk.
- Upgrade Authority: Who holds the keys to the smart contract? If the operator can upgrade the contract unilaterally, the "non-custodial" label is a misnomer.
As of September 10, 2026, the industry continues to grow, with major players like MoneyGram and Western Union launching stablecoin-backed programs. However, the August incident serves as a stark reminder that scale does not equal security. The rapid refunding of Avici users by Rain was a fortunate outcome for those involved, but it was a result of corporate policy, not a inherent feature of the underlying financial technology. Investors and users alike should recognize that in the current market, the distance between a successful transaction and a total loss of funds is often just a single line of vulnerable code.