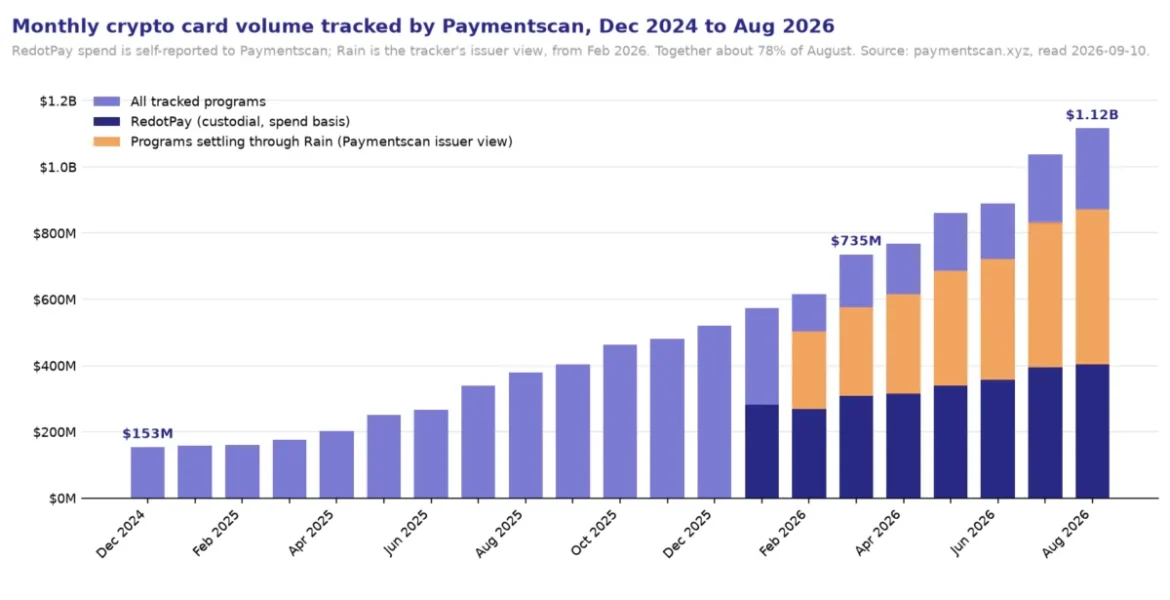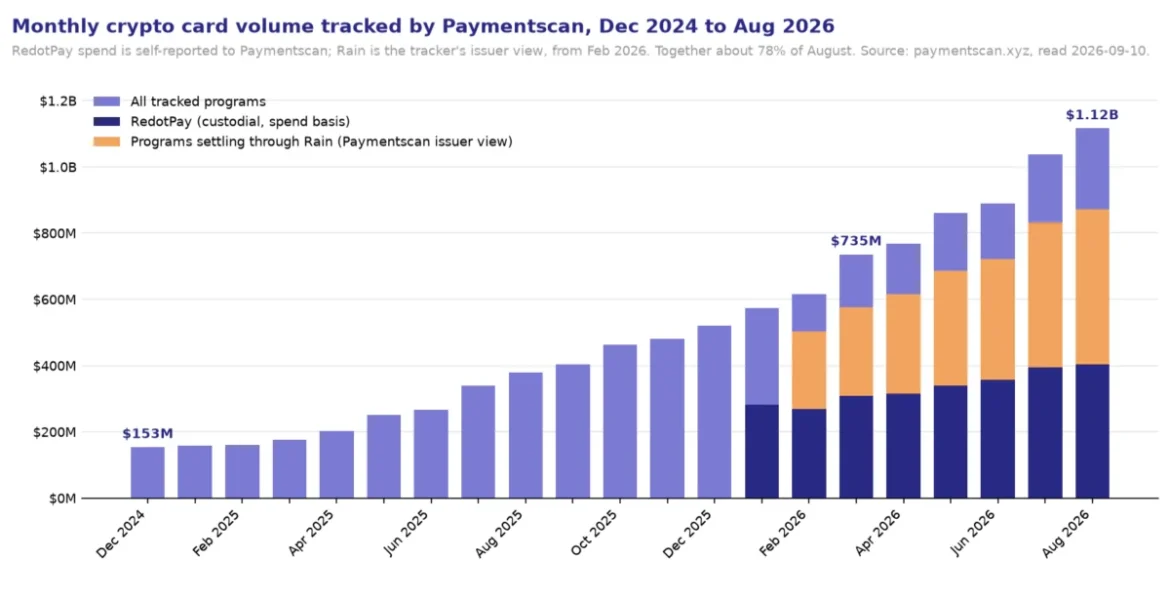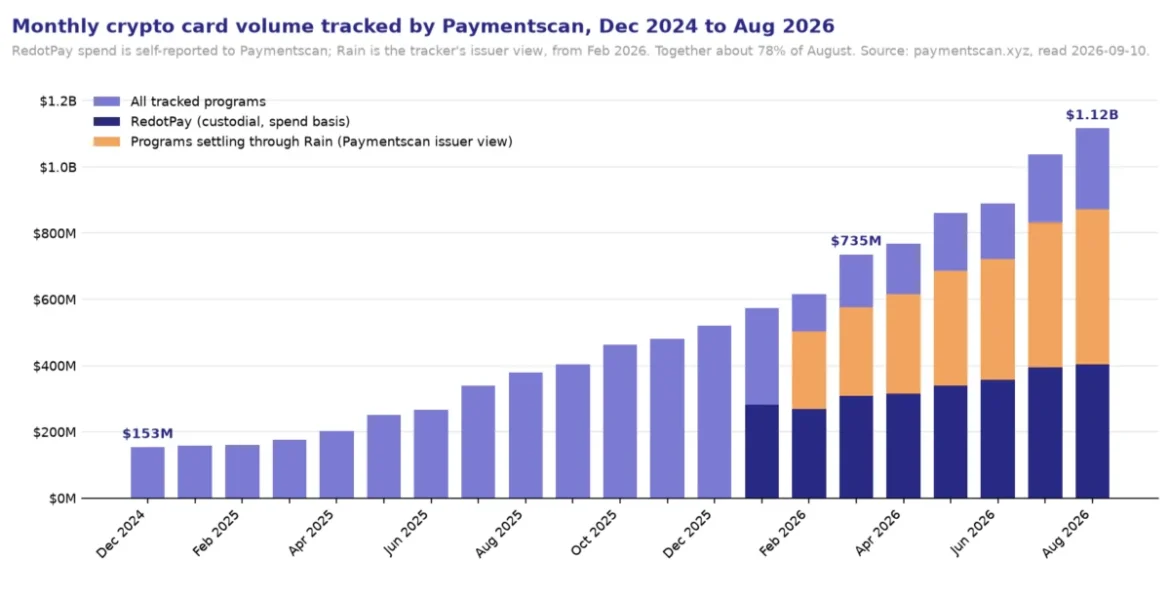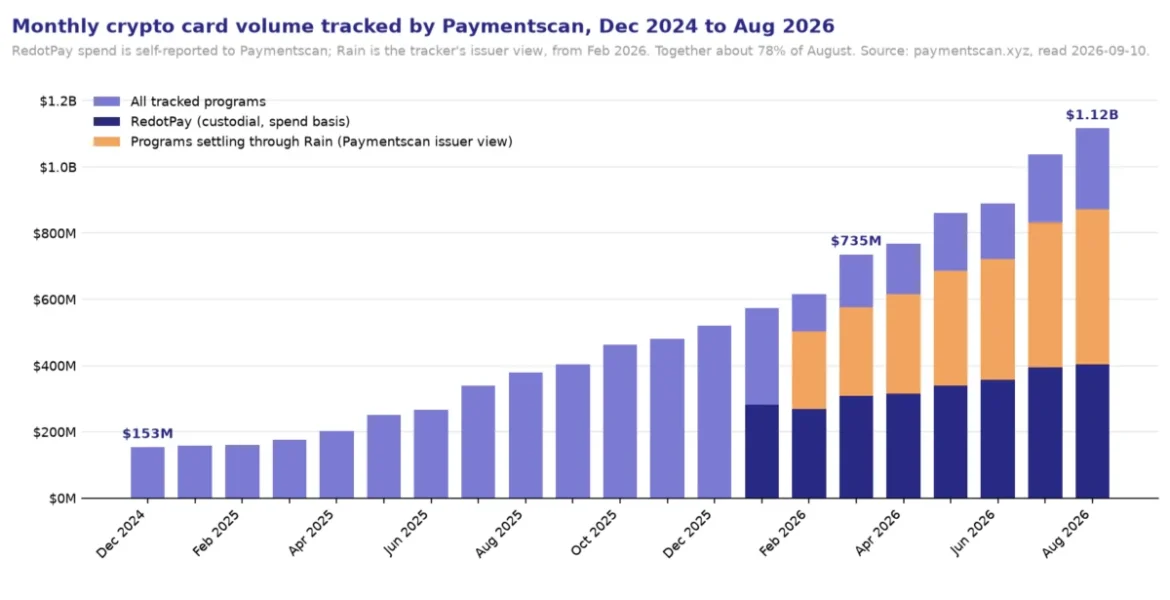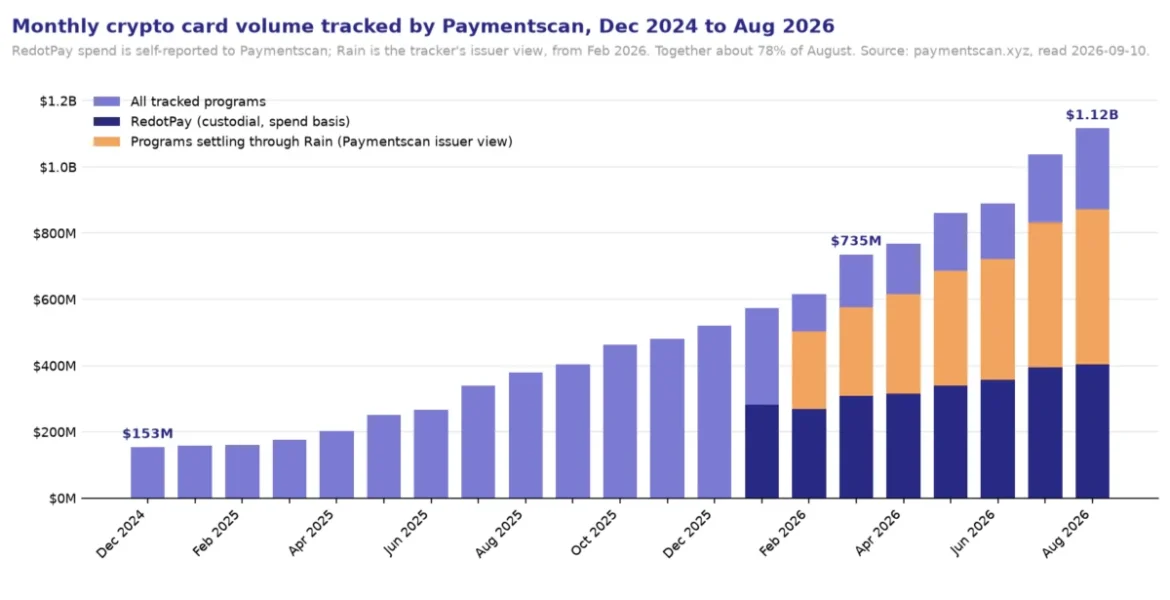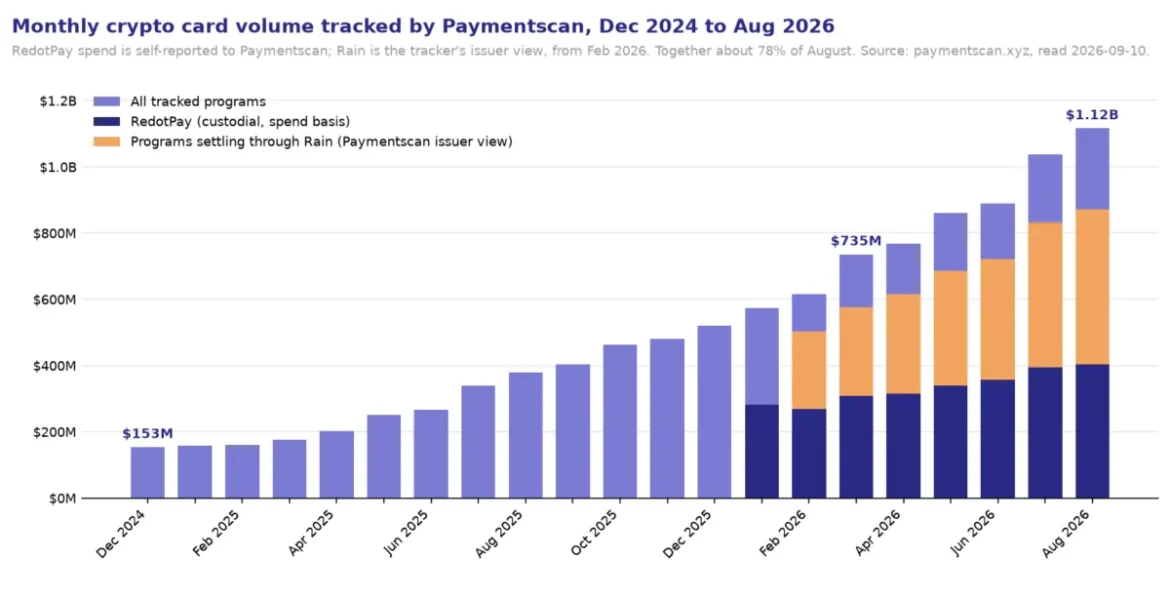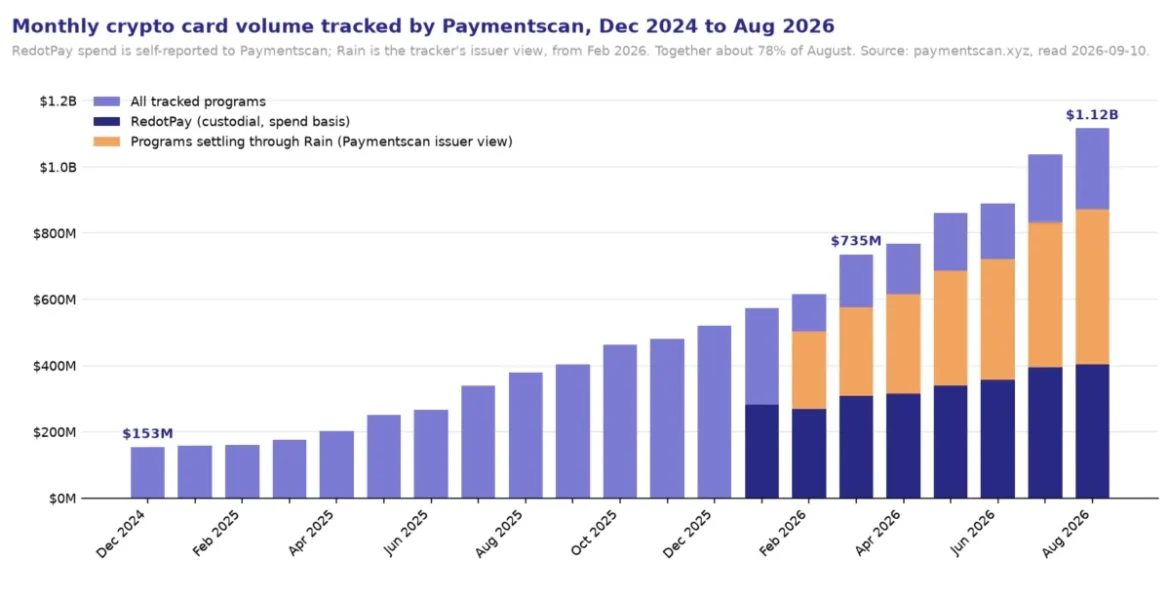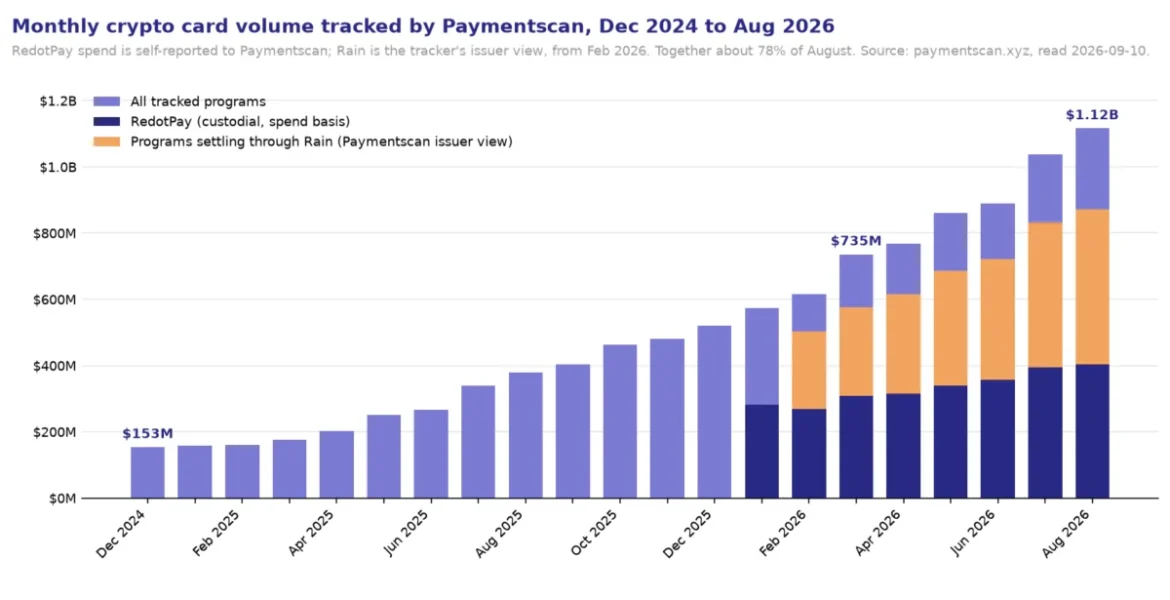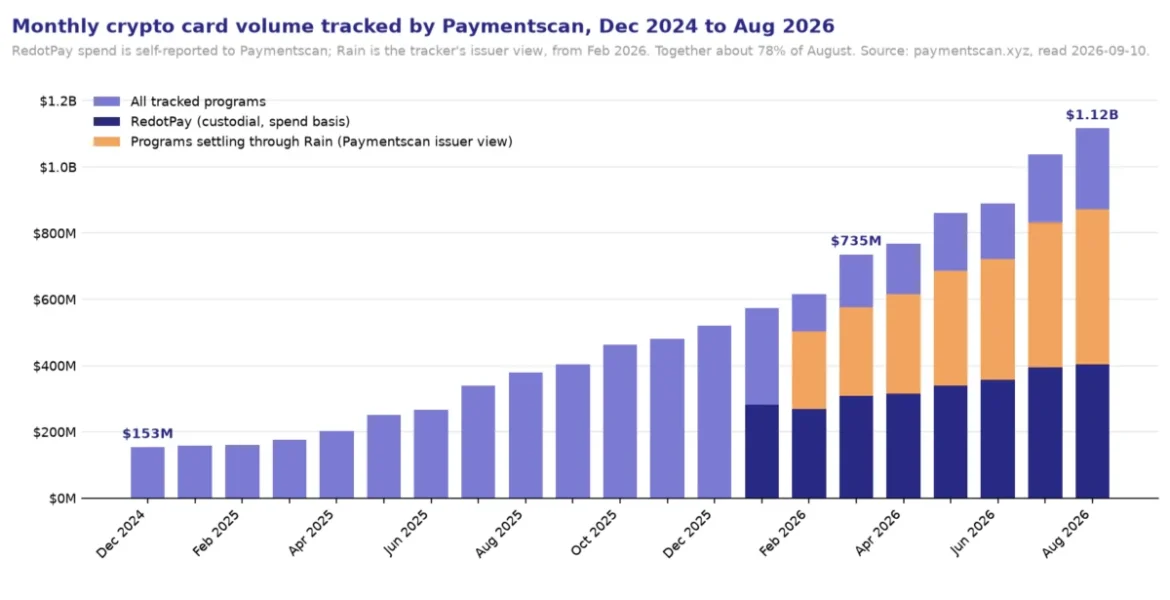
At 16:49:48 UTC on Friday, August 28, 2026, a Solana-based digital wallet—funded only three hours earlier with 1.79 SOL purchased via a modest $190 USDC bridge—initiated a sophisticated, programmatic drain of user card-balance accounts held by Avici, a prominent Solana-based neobank. By the time the exploit concluded, 1,685 users had seen a combined $500,859.22 siphoned from their accounts. This event, while contained, sent shockwaves through the rapidly expanding $1.1 billion-a-month crypto debit card sector, exposing significant vulnerabilities in the architecture of "non-custodial" financial products.
The incident targeted a specific smart contract architecture used by Avici and several other programs, all of which relied on infrastructure provided by Rain, a dominant player in the self-custodial card market. While Avici’s terms of service, last updated in June 2025, explicitly stated that neither Avici nor its issuer held custody of client collateral, the reality of the technical implementation proved more precarious. The funds were held in a smart contract that, while ostensibly user-controlled, remained susceptible to administrative upgrades and logic flaws that bypassed the users’ own keys.
A Chronology of the August 28 Exploit
The breach was not a result of compromised user private keys or a phishing attack on individual customers. Instead, it was a precise authorization exploit. Investigation of on-chain data shows the attacker’s wallet (FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj) executed 21,405 transactions within a window of approximately two and a half hours, with roughly 17,500 succeeding.
The attacker utilized a vulnerability in the signature-verification logic of the Rain-controlled Solana program. By manipulating the Ed25519 signature-verification instruction, the attacker successfully tricked the contract into accepting a single signature as the two required approvals for administrative actions. This effectively granted the attacker administrative control over over a thousand individual collateral accounts. Once elevated to "collateral admin" status, the attacker systematically invoked the WithdrawCollateralAsset function.
The financial impact was swift. The attacker converted the stolen assets into approximately 1.11 million USDC, which was then bridged to Ethereum and funneled through Tornado Cash in a standard laundering sequence. The entire operation was completed within hours, leaving the victims with no recourse through traditional banking channels.
The Response and Remediation
Despite the severity of the loss, the immediate aftermath was marked by a swift, albeit private, recovery effort. Avici reported that all 1,685 affected users were made whole within 24 hours. The capital for these refunds was provided by Rain, the underlying infrastructure provider, which also facilitated a 10% bonus for affected Avici and Tria users as a gesture of good faith.
Rain moved quickly to patch the vulnerability. By 19:18 UTC, mere minutes after the final malicious transaction, the first patch was deployed. By September 5, Rain had successfully migrated the upgrade authority for all affected programs to a Squads multisig vault, adding a layer of multi-party security that had been absent at the time of the hack. However, the lack of a public post-mortem remains a point of contention for security researchers and industry observers, who argue that such transparency is essential for maintaining trust in the "non-custodial" label.

The Ecosystem: Custody and Risk
The August breach highlights a critical misconception regarding the term "non-custodial." In the context of 2026 crypto cards, the term describes who cannot move funds under normal conditions, but it often obscures who holds the "upgrade keys" to the underlying smart contracts.
The industry currently operates under five distinct custody models, each carrying unique risk profiles:
- Sold to the Operator: Assets are effectively sold to the provider in exchange for a debt claim. KAST is the most prominent example, where users hold an enforceable claim against the operator’s treasury, placing them behind senior debt in the event of bankruptcy.
- Nominee Custody: Platforms like Revolut hold legal title on behalf of the user. While this offers some regulatory protection, it remains a centralized model.
- Fiat Conversion: Exchanges like Crypto.com and Kraken convert crypto to fiat at the moment of the swipe. The crypto remains in exchange custody, while the fiat is held by licensed banking partners, subject to e-money safeguarding regulations.
- Program-Managed Contracts: This is the category Avici, Tria, and Rain occupied. Users "own" their collateral in a smart contract, but the program manager holds the administrative authority to upgrade that contract.
- Direct Vault Access: Models like Gnosis Pay and Ether.fi Cash represent the highest level of security, where funds are held in user-controlled vaults that the operator cannot unilaterally move, even if they wanted to.
Market Concentration and Regulatory Concerns
The reliance on a single infrastructure provider—Rain—has become a structural reality of the crypto card market. Seven of the 18 programs analyzed, including KAST, Avici, Ether.fi, and Tria, name "Third National" as their card issuer. Third National is not a bank, but a Puerto Rico-licensed money transmitter and a subsidiary of the Rain group.
This concentration of power means that systemic risks are shared across a wide swath of the industry. While the August exploit was limited to specific Solana-based contracts, the fact that a single bug could impact multiple independent-seeming neobanks demonstrates a hidden fragility in the sector.
Furthermore, the "no-KYC" (Know Your Customer) card market remains a wild west of shifting regulatory standards. Many of these cards operate in a gray area, exploiting the gap between corporate entity verification and individual user verification. As EU Regulation (EU) 2024/1624 approaches its July 2027 implementation date, the window for these anonymous, crypto-loaded cards is rapidly closing. The new regulations will effectively outlaw anonymous reloadable cards and place significant pressure on offshore issuers, likely forcing a wave of consolidation and shutdowns.
Broader Implications for the Industry
The failure of several high-profile programs in 2026—including the wind-down of Kulipa’s infrastructure and the suspension of services by Fiat24—underscores that the primary risk to crypto cardholders is not always a hack, but the potential for sudden service termination. When an infrastructure provider or a licensed issuer decides to wind down, the "non-custodial" nature of these cards provides a safety net for assets, but it does not prevent the loss of the product itself.
The Gnosis Pay transition, which saw the shutdown of its consumer interface in favor of a white-label platform, suggests that the market is moving toward institutional-grade infrastructure. The consumer-facing layer is volatile, but the underlying primitives—smart contract-based spending and just-in-time fiat conversion—are becoming industry standards.
As of September 2026, the crypto card market has reached a critical maturity threshold. With $1.1 billion in monthly volume, it is no longer a niche curiosity. However, the August exploit serves as a stark reminder that "on-chain" does not automatically equate to "secure." The future of the industry depends not only on the performance of the cards but on the integrity of the smart contracts that hold the collateral and the transparency of the issuers who provide the gateway to the traditional financial system. For the average user, the lesson is clear: until the technical documentation is public and the upgrade authority is decentralized, the "non-custodial" card is only as secure as the company behind it.