The rapid acceleration of artificial intelligence adoption across the financial services sector has brought unprecedented operational efficiencies, yet it has simultaneously exposed institutions to a complex maze of interconnected vulnerabilities. As banks, asset managers, and insurance providers race to deploy generative and predictive models, industry stakeholders find themselves under mounting pressure to comprehend how these emerging technologies alter their overarching risk profiles. Recent empirical data underscores this growing apprehension. According to comprehensive research conducted by Parker & Lawrence Research, an overwhelming 60% of financial sector respondents now classify AI-related technology risk as "high or greater." This statistic serves as a stark warning flare, reinforcing an urgent industry-wide demand for more sophisticated, automated methodologies that can seamlessly connect disparate risk data streams and pinpoint critical changes requiring immediate executive attention.
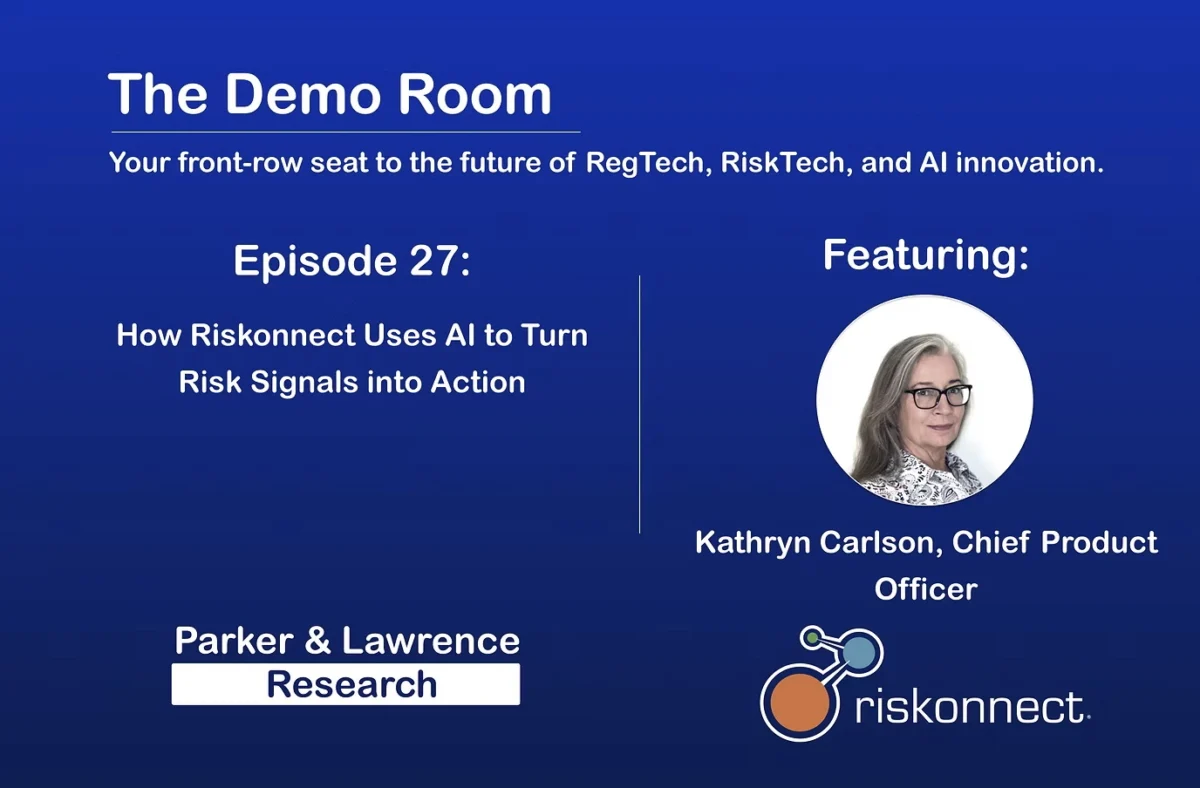
This heightened sense of urgency forms the thematic bedrock of the upcoming AI in Risk and Compliance 2026 report. Jointly produced by RegTech Analyst and Parker & Lawrence Research, the exhaustive publication investigates how pioneering technology vendors are engineering next-generation tools to empower financial institutions. These software solutions are explicitly designed to fortify internal risk identification, rigorous assessment protocols, and continuous regulatory oversight. Within this overarching research initiative, Parker & Lawrence’s ongoing spotlight series—appropriately titled "The Demo Room"—has turned its analytical lens toward Riskonnect, a prominent enterprise risk management provider offering an Integrated Risk Platform meant to shatter traditional corporate silos.
The Chronology of Modern Risk: From Periodic Checkpoints to Continuous Oversight
To fully appreciate the innovations driving modern risk technology, one must examine the historical evolution of how financial institutions have managed operational and technological threats. For decades, the industry relied heavily on periodic assessments, static inventories, and massive, disjointed spreadsheets. Under this legacy framework, risk management was treated as a cyclical event rather than an ongoing operational discipline. Technology teams conducted annual or quarterly audits, compliance officers reviewed regulatory updates in isolation, and cybersecurity divisions maintained separate logs of critical digital assets and third-party dependencies.
As the digital landscape matured through the 2010s, this fragmented approach began to show severe structural cracks. The advent of cloud computing, microservices architectures, and intricate third-party vendor ecosystems meant that corporate technology stacks were no longer static; they evolved daily, if not hourly. Yet, risk management practices largely remained anchored to manual, point-in-time reviews.
The entry of artificial intelligence into the corporate mainstream has pushed these legacy systems past their breaking point. Modern financial organizations must now govern thousands of individual machine learning models, vast and fluid data pipelines, and complex webs of third-party software dependencies. Traditional assessment frameworks simply lack the granular velocity required to capture these modern threat vectors. Recognizing this paradigm shift, RegTech Analyst and Parker & Lawrence Research initiated their collaborative study in late 2025, mapping out how the regulatory technology landscape is adapting to these unprecedented challenges through the lens of platforms like Riskonnect.
The Anatomy of Fragmentation: Why Disconnected Data Threatens Financial Stability
The fundamental challenge facing risk professionals today is not a lack of data, but rather the profound disconnection of that data across corporate departments. In a typical financial institution, operational silos run deep. Technology infrastructure teams maintain asset and configuration databases; risk management departments oversee internal controls and risk assessments; and compliance units labor to interpret a relentless wave of global regulatory changes. Meanwhile, specialized functions such as cybersecurity, operational resilience, internal audit, and third-party risk management maintain their own proprietary records of critical services and interdependencies.
When these departments operate in informational vacuums, the institution loses its unified field of vision. A minor modification in a third-party software library, for instance, can quietly compromise multiple internal controls simultaneously. Similarly, a sudden regulatory update might alter the compliance requirements attached to core data storage assets, while a supplier failure could threaten the operational resilience of vital customer-facing services.
Under the old paradigm, identifying these cascading relationships required painstaking manual investigation. Risk teams frequently found themselves bogged down reassessing low-impact operational changes while accidentally overlooking more insidious, high-level vulnerabilities. Preparing formal impact statements, drafting mitigation plans, and updating control mappings demanded hours of tedious administrative labor, diverting skilled professionals from strategic decision-making.
Furthermore, the hasty introduction of basic AI assistants or ungrounded conversational language models has historically failed to resolve these systemic weaknesses. When large language models are left to operate on incomplete, out-of-date, or siloed enterprise data, they frequently generate plausible-sounding yet dangerously inaccurate risk assessments—a phenomenon commonly known in the industry as AI hallucination. True, effective AI-driven risk management cannot exist in a vacuum; it requires a robust foundation of structured enterprise data, dependable change-detection signals, and explicitly mapped relationships between every record that informs an executive decision.
Context-Aware Technology Risk: Inside the Riskonnect Framework
Addressing the core architectural flaws of legacy risk management requires a synthesis of structured relational data and advanced artificial intelligence. Riskonnect’s approach within its Integrated Risk Platform focuses heavily on establishing a context-aware technology risk workflow. Rather than treating AI as a standalone magic bullet, the platform embeds rules-based data preparation, retrieval-grounded language models, and specialized AI agents directly into the day-to-day operations of risk and compliance teams.
At the heart of this architecture lies a centralized, connected data model. This framework systematically links technology assets, inherent risks, internal controls, root causes, potential consequences, security incidents, corporate policies, regulatory mandates, and all related audit trails. By unifying these relational data points, the platform provides risk professionals with immediate contextual depth during assessments, effectively eliminating the need to manually cross-reference spreadsheets across different departments.
The workflow itself follows a meticulously structured, multi-layered progression designed to maximize safety and auditability:
- Deterministic Data Preparation: When a change occurs within the enterprise technology environment, rules-based processes automatically identify the alteration and assemble all relevant historical and contextual records. This ensures that the foundational data processing remains entirely consistent, predictable, and fully auditable.
- AI-Driven Materiality Assessment: Once the relevant records are collated, Riskonnect’s specialized "Risk Signal Agent" evaluates the specific change against the organization’s predefined risk appetite, asset criticality thresholds, and overarching governance frameworks. The agent then provides a data-backed recommendation on whether a formal reassessment is necessary, complete with an explicit, traceable rationale for its conclusion.
- Human-in-the-Loop Oversight: Crucially, the platform enforces strict human governance. Automated agents do not unilaterally alter risk registries or close compliance tickets; instead, human reviewers retain absolute authority to accept or reject all consequential actions. This ensures that material risk decisions remain firmly under the stewardship of qualified human professionals.
- Retrieval-Grounded Policy Analysis: To bridge the gap between internal operations and external law, the platform employs retrieval-grounded models that continuously cross-examine internal corporate policies against newly released regulatory requirements. These models pinpoint compliance gaps, articulate their business significance, and automatically translate findings into actionable tasks for technology risk teams.
Driving Operational Efficiency and Strategic Response
Beyond merely identifying and assessing vulnerabilities, modern risk technology must actively assist organizations in formulating and executing effective responses. Riskonnect’s platform extends its capabilities deep into the remediation phase, enabling teams to rapidly draft comprehensive risk descriptions, formalized risk appetite statements, rigorous business impact assessments, customized mitigation plans, operational playbooks, and suggested control updates within a standardized corporate format.
Once these response documents are drafted, autonomous AI agents can coordinate subsequent remediation activities, multi-stage peer reviews, and policy updates across designated stakeholders. This seamless orchestration allows risk departments to transition rapidly from the passive identification of potential issues to the active, coordinated management of organizational resilience.
According to internal company metrics reported by Riskonnect, this automated, context-aware workflow can dramatically accelerate compliance operations, reducing the time required for personnel to understand and digest unfamiliar regulatory frameworks by more than 80%. Additionally, the firm highlights substantial reductions in operational labor costs alongside significantly earlier identification and remediation of technology risks.
Independent market observers, including analysts at Parker & Lawrence Research, have emphasized that continuous materiality assessment represents the most compelling aspect of this technological shift. By moving away from the outdated assumption that every minor IT change demands an identical level of intense scrutiny, platforms like Riskonnect allow financial institutions to intelligently triage developments based on true business impact. Risk professionals can instantly determine which operational changes warrant a comprehensive re-evaluation, understand precisely why those changes matter, and deploy targeted remediation strategies with unprecedented speed.
Analytical Implications: The Balance of Automation and Governance
While the integration of artificial intelligence into enterprise risk management offers transformative potential for the financial services sector, industry analysts urge a balanced, pragmatic perspective. The long-term success of these advanced platforms depends heavily on foundational data hygiene. Organizations with fragmented asset inventories, poorly mapped dependency networks, or historically neglected risk registers will inevitably struggle to extract full value from AI-driven automation. As the software engineering adage warns: "garbage in, garbage out."
Furthermore, financial institutions must demand rigorous empirical proof that autonomous AI agents can reliably differentiate between routine background IT activity and genuinely material risk signals without bombarding compliance departments with alert fatigue. Proposed AI-generated remediation strategies must remain strictly tethered to internal corporate policies, external legal obligations, and board-approved risk appetites.
Despite these necessary caveats, the broader trajectory is unmistakably clear. As artificial intelligence continues to expand and complicate the enterprise technology footprints that financial institutions must govern, the ability to seamlessly connect disparate risk signals and execute continuous, context-aware oversight will transition from a competitive advantage to an absolute survival requirement.
The collaborative insights generated by RegTech Analyst and Parker & Lawrence Research—highlighted through platforms such as Riskonnect—illustrate a vital path forward. By thoughtfully marrying structured enterprise data, deterministic rules, retrieval-grounded AI models, and unwavering human governance, financial services organizations can finally step away from the precarious rigidity of periodic risk assessments and step confidently into a secure, resilient, and continuously managed future.