On March 26, 2026, the Canadian regulatory landscape underwent a seismic shift when Bill C-12 received Royal Assent. This legislation introduced significant amendments to the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA), effectively resetting the compliance benchmark for all reporting entities across the nation. By mandating that anti-money laundering (AML) programs be "reasonably designed, risk-based and effective," the federal government has moved beyond a "check-the-box" regulatory environment toward a performance-based oversight model.
The implications for Canadian firms are severe. Under the new framework, penalties for non-compliance have increased forty-fold. For organizations that fail to demonstrate the operational efficacy of their programs, the financial consequences are substantial: cumulative fines are now capped at the greater of C$20 million or 3% of an entity’s gross global revenue. This legislative pivot signifies that the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) is no longer merely auditing the existence of policies; it is rigorously testing the outcomes of those policies in practice.
A Chronology of the Legislative Shift
The journey toward the current regulatory standard began well before the March 2026 enactment. For years, the Canadian government faced pressure from international bodies, including the Financial Action Task Force (FATF), to close loopholes regarding transparency and the effectiveness of AML reporting.
- Pre-2026: FINTRAC operated under a framework that prioritized the existence of written compliance manuals and mandatory training records. While transaction reporting was required, the "effectiveness" of these systems was often measured by their adherence to procedural guidelines rather than their ability to stop illicit financial flows.
- March 2026: Bill C-12 receives Royal Assent, codifying the "effectiveness" standard into law.
- May 2026: FINTRAC publishes updated administrative monetary penalty (AMP) guidance, explicitly shifting the focus of assessments toward operational performance and risk-based outcomes.
- September 2026: Six months into the new regime, industry leaders and regulators begin to assess the reality of the post-C-12 landscape, noting a distinct increase in the frequency and depth of FINTRAC examinations.
The New Standard: Effectiveness Over Efficiency
The core challenge for financial institutions today lies in the distinction between efficiency and effectiveness. Industry experts, including Claude Baksh, Co-founder and President of Grace CSI, have noted that an efficient system—one that processes high volumes of data quickly—does not inherently mean an effective one.
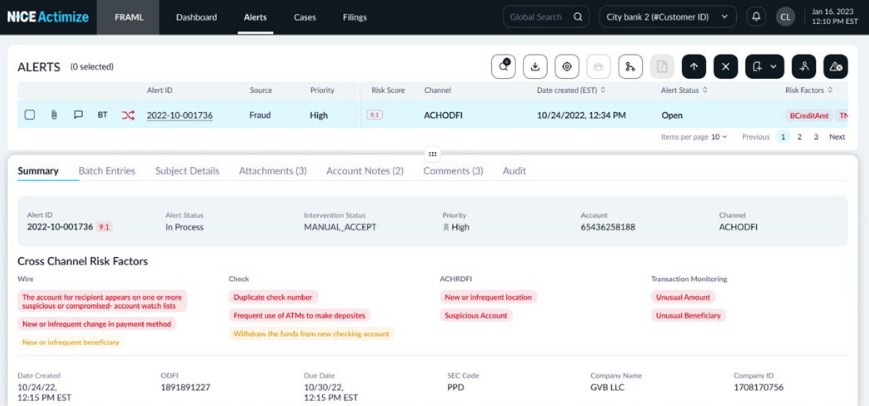
"You can have an efficient system that delivers garbage versus an effective system," Baksh stated during a recent industry webinar. This distinction is most visible in the management of alert backlogs. Under the previous regime, many firms maintained large backlogs of transaction alerts, treating them as a manageable operational cost. Under the new standard, such backlogs are viewed as prima facie evidence of an ineffective program. If a firm’s monitoring system is so overwhelmed that it cannot distinguish between routine activity and suspicious transactions, it is failing to meet its statutory requirements.
Andrew Davies, Global Head of Financial Crime Compliance (FCC) Strategy at ComplyAdvantage, echoed this sentiment, arguing that the volume of alerts is now a liability rather than a metric of activity. "If you’re overwhelmed with alerts, if you’ve got that huge operational backlog, how can you possibly be effective?" Davies questioned. The regulator now views the absence of clear, timely, and actionable Suspicious Transaction Reports (STRs) as a signal of a systemic failure, regardless of how many transactions were screened.
Data-Driven Enforcement and Peer Benchmarking
FINTRAC is increasingly utilizing cross-entity data to establish industry-wide benchmarks. By comparing firms with similar risk profiles, product offerings, and customer bases, regulators are identifying outliers. If a financial institution files significantly fewer STRs than its peers, that institution is now automatically flagged for a deeper examination.
This shift suggests that the regulator is looking at the entire ecosystem. Reporting output is now being used as direct evidence of a program’s health. For firms, this means the days of operating in a silo are effectively over. The regulator expects institutions to justify their filing rates based on their specific risk exposure, rather than relying on historical averages or industry-wide trends that may not accurately reflect their unique client base.
The Technical Debt of Legacy Infrastructure
Research from the State of Financial Crime 2026 report highlights a significant barrier to this new standard: infrastructure. Approximately 35% of Canadian firms report that their ability to screen customers against sanctions and watchlists is hampered by limitations in their technology stack. The average firm in the sector currently runs more than six separate screening solutions, many of which are fragmented, legacy systems that do not communicate effectively with one another.
These siloed operations result in inconsistent data definitions and "static" rules that fail to capture real-time threat typologies. When a firm uses off-the-shelf rules without tailoring them to its specific risk environment, the result is an influx of "noise"—thousands of false positives that distract human analysts from high-risk activity.
To adapt, institutions must move toward a unified ingestion process. Data consistency is the prerequisite for any recalibration of thresholds. Without a clean, centralized data pipeline, firms cannot hope to explain to an examiner why similar products generate wildly different alert volumes across their various platforms.
Documentation and the Requirement of Explainability
For financial institutions, the burden of proof has shifted entirely to the entity. To survive an examination under the new PCMLTFA requirements, firms must be prepared to provide a "narrative of evidence." This includes three key pillars:
- Documented Risk Assessments: Every detection scenario and rule running in production must be linked back to a thorough, documented risk assessment.
- Audit Logs of Threshold Adjustments: Firms must maintain logs explaining why specific thresholds were adjusted, when they were changed, and how these changes align with the evolving threat landscape.
- End-to-End STR Trails: When a high-priority alert is generated, the firm must be able to walk an examiner through the decision-making process. If the alert was dismissed, there must be a factual, plain-language explanation for why it was deemed non-suspicious.
"You’ve got to have notes on your files," Baksh emphasizes. "You can’t just have automated decisions being made without that plain language explanation that’s factual, that you can defend."
This requirement for "explainability" also extends to the use of artificial intelligence and machine learning models. If a model informs a compliance decision, that model must be subject to rigorous validation, bias testing, and drift management. Furthermore, firms are expected to retain historical model versions to allow regulators to reconstruct past decisions.
Implications for Future Strategy
The budgetary pressure on compliance departments is intensifying as they compete for resources with other business units. However, experts suggest that the most successful firms are those that frame AML compliance as a broader strategic asset.
By integrating AML systems with fraud detection and market segmentation data, firms can gain a clearer picture of customer behavior. "Your AML system has historically got a lot of information about your customers and their behavior," says Andrew Davies. "Let’s look at that behavior through a different lens, and maybe there’s business opportunity there."
The path forward for Canadian financial institutions is clear: the focus must move from the mere appearance of compliance to the demonstrable reality of it. The institutions best positioned to succeed in the coming years will be those that prioritize data integrity, invest in scalable technology, and foster a culture of explainability. As FINTRAC continues to sharpen its examination criteria, the ability to clearly articulate the "why" behind every automated decision will be the definitive measure of a successful financial institution in Canada.