On March 26, 2026, the legislative landscape for financial crime prevention in Canada underwent a fundamental transformation as Bill C-12 received Royal Assent. This pivotal legislation amended the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA), effectively ushering in a new era of regulatory scrutiny for Canadian financial institutions and reporting entities. For years, the Canadian regulatory environment was defined by its adherence to procedural compliance—ensuring that policies, training, and documentation existed on paper. Today, the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) has shifted its mandate toward a standard of "operational effectiveness," compelling firms to prove that their anti-money laundering (AML) programs not only exist but actually succeed in identifying and mitigating financial crime.
The legislative change, which arrived following intense discussions between the federal government and financial industry stakeholders, represents the most significant recalibration of AML requirements in over a decade. Under the new regime, the threshold for failure has been significantly raised. The federal government, seeking to bolster Canada’s global reputation as a secure financial hub, has increased potential financial penalties by a factor of forty. These cumulative fines are now capped at the greater of C$20 million or 3% of a firm’s gross global revenue, a move designed to ensure that compliance is treated as a core strategic pillar rather than a back-office burden.
A Chronology of the Regulatory Shift
The journey toward the current regulatory standard began well before the 2026 amendments. For several years, international bodies like the Financial Action Task Force (FATF) had been pushing for increased transparency and efficacy in Canada’s AML regime.
- Pre-2025: Regulatory focus remained heavily centered on "technical compliance"—the existence of written policies, procedures, and internal controls.
- Early 2025: Discussions surrounding the strengthening of the PCMLTFA intensified as the federal government sought to address gaps in the monitoring of real-time payment systems and digital asset transfers.
- March 26, 2026: Bill C-12 receives Royal Assent, codifying the requirement that compliance programs must be "reasonably designed, risk-based, and effective."
- May 2026: FINTRAC releases updated administrative monetary penalty guidance, explicitly signaling that the regulator will prioritize outcomes over documentation.
- September 2026: Six months post-enactment, initial enforcement data confirms that firms are being penalized not for missing paperwork, but for the failure to file Suspicious Transaction Reports (STRs) when evidence existed to suggest they were warranted.
The Shift from Efficiency to Effectiveness
In the professional compliance sector, the distinction between efficiency and effectiveness has become the primary point of contention. Industry experts, including Claude Baksh, Co-founder and President of Grace CSI, have noted that many firms historically mistook "processing speed" for "compliance quality." A system that processes thousands of alerts per day might be highly efficient from an operational standpoint, yet it remains fundamentally ineffective if it fails to generate high-quality, actionable intelligence for law enforcement.
The "garbage in, garbage out" problem continues to plague legacy systems. Many institutions operate on fragmented, siloed platforms where data definitions are inconsistent across different business lines. When these systems are combined with static, off-the-shelf rule engines, they generate an overwhelming volume of "noise"—false positives that drown out legitimate threats. Andrew Davies, Global Head of FCC Strategy at ComplyAdvantage, emphasizes that in a world of near-instantaneous financial transactions, legacy technology is increasingly a liability. If a firm’s monitoring tools cannot react at the speed of the payments they are supposed to be screening, they are, by definition, failing the effectiveness test.
FINTRAC’s New Assessment Methodology
The current approach taken by FINTRAC is far more analytical and comparative than in previous years. The regulator is now performing broad benchmarking across industry sectors. By leveraging cross-entity data, FINTRAC establishes a baseline of expectations for firms that offer similar products and operate within similar risk profiles.
If a financial institution is filing significantly fewer STRs than its peers, it is now an immediate red flag. Such discrepancies trigger closer scrutiny, as the regulator assumes that the firm is either under-reporting or lacks the technical capacity to identify suspicious behavior. As Baksh notes, reporting output is now treated as direct evidence of a program’s health. If a firm’s alerts are not converting into meaningful reports, auditors are likely to question the governance, model validation, and threshold logic underpinning the entire system.
The Data Gap: Why Fragmentation Fails
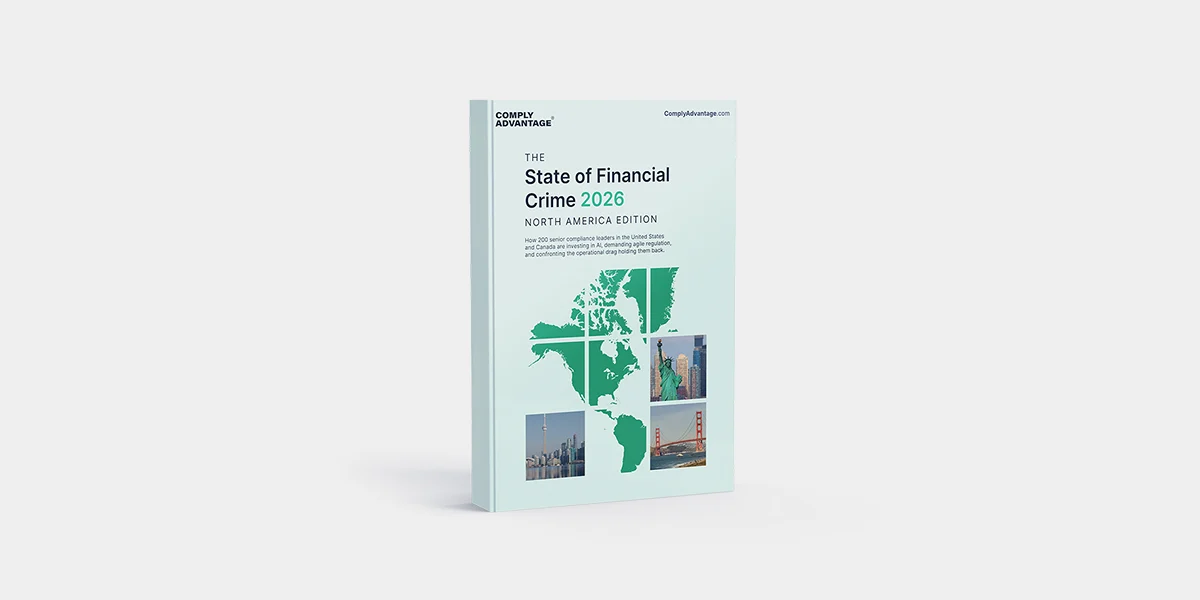
According to the "State of Financial Crime 2026" research, nearly 35% of Canadian firms report significant limitations in their ability to screen customers against sanctions and watchlists. A major contributor to this struggle is the reliance on multiple, disjointed screening solutions. The average firm in the study reported using more than six separate systems to manage their AML obligations.
This fragmentation creates a "explainability" crisis. When an examiner asks why a specific transaction was not flagged, or why different business units are generating disparate alert volumes for the same product, a firm must be able to provide a coherent, data-driven answer. The ability to "walk the trail" from the initial risk assessment to the detection scenario, and finally to the resulting STR or dismissal, is now a mandatory expectation. Firms that cannot provide a plain-language, factual explanation for their automated decisions are finding themselves in an indefensible position.
Evidence-Based Compliance: What Firms Must Now Provide
To navigate the new regulatory reality, financial institutions must move toward a model of "defensible compliance." This requires several tactical adjustments:
- Documented Risk Assessments: Every detection scenario and production rule must be explicitly mapped to the firm’s documented risk assessment. It is no longer acceptable to run automated systems without clear, written justification for why specific thresholds were chosen.
- Drift Management and Explainability: As threat typologies evolve, so must a firm’s detection models. Firms are expected to maintain logs explaining why thresholds were adjusted over time. These logs must be auditable, showing how the firm responded to changes in customer behavior or emerging financial crime trends.
- Model Validation and Human-in-the-Loop: While automation is necessary for scale, it cannot be a "black box." FINTRAC expects firms to retain historical model versions that can be re-run for audit purposes. Furthermore, the "human-in-the-loop" approach is now essential for all high-risk decisions, ensuring that automated outputs are verified by human expertise.
- Integrated Data Ingestion: Before adjusting thresholds, firms must ensure that their data ingestion processes are unified. Consistent data definitions across the organization are the prerequisite for effective model performance.
The Business Case for Compliance Investment
For many organizations, the pressure to meet these new standards is being used as a catalyst to secure additional budget for technology upgrades. The argument for investment is strongest when it is framed as a benefit to the entire enterprise, rather than just the compliance department.
When an AML program is optimized—reducing false positives and improving data accuracy—the secondary benefits are substantial. These include more efficient customer onboarding, better fraud detection, and deeper insights into market and product segmentation. By viewing AML data as a strategic asset rather than a regulatory burden, firms can identify business opportunities while simultaneously lowering their risk profile.
Implications for the Future of Canadian Finance
The implementation of Bill C-12 has essentially ended the era of "check-the-box" compliance in Canada. The bar has been moved from intent to impact. The financial industry is now faced with the challenge of transitioning from legacy architectures to agile, data-driven systems capable of real-time monitoring and transparent decision-making.
As the industry moves further into this new regulatory cycle, the firms that will succeed are those that embrace "explainability." Whether through the use of advanced analytics, artificial intelligence, or human-led oversight, the mandate is clear: Canadian institutions must be able to demonstrate, through verifiable evidence, that they have the capability to detect the evolving methodologies of modern financial criminals. In the eyes of FINTRAC, if a program cannot prove its own effectiveness, it is not simply a failing of technology—it is a risk to the integrity of the entire Canadian financial system. For those who remain in the "legacy mindset," the risk of significant financial penalties and long-term reputational damage is no longer a distant possibility, but a present reality.