
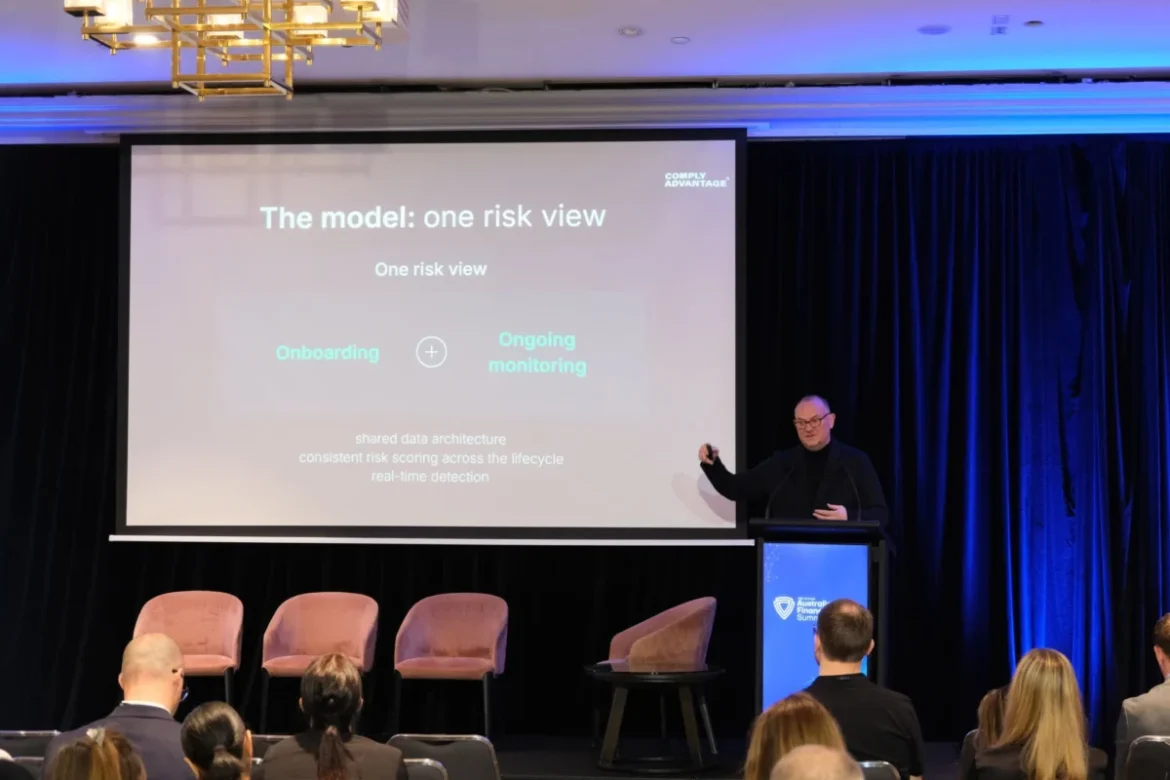
The pursuit of effectiveness has become the singular focus for financial regulators and compliance officers globally, signaling a fundamental shift in how institutions must approach the escalating threat of financial crime. At the Australian Financial Crime Summit (AFCS) held in Sydney on September 1, 2026, industry leaders converged to address a stark reality: the current fragmentation of compliance infrastructure is no longer tenable. Andrew Davies, Global Head of Financial Crime Compliance (FCC) Strategy at ComplyAdvantage, delivered a keynote address highlighting that compliance teams remain fundamentally unable to prove their effectiveness as long as onboarding processes and ongoing transaction monitoring exist in isolated, non-communicative systems. This structural deficiency is not merely an operational inconvenience; it is a systemic vulnerability that organized crime syndicates are actively exploiting.
The Australian financial landscape is currently navigating a period of unprecedented regulatory pressure. The National Anti-Scam Centre reported that Australians lost a staggering $2.18 billion to scams in 2025, a figure derived from over 274,000 loss-bearing reports. This data point serves as a bellwether for the broader challenges facing financial institutions. As noted in the AUSTRAC Money Laundering Update 2026, the complexity of illicit activity is surging, driven by the adoption of sophisticated, AI-enabled document fraud and automated synthetic identities. This environment of heightened risk is occurring simultaneously with the implementation of the Tranche 2 AML/CTF obligations, which came into effect on July 1, 2026. This regulatory expansion has brought approximately 80,000 previously unregulated businesses—including real estate agents, lawyers, and accountants—into the formal AML/CTF scope, significantly broadening the perimeter that must be defended.
The regulatory roadmap for the coming year is equally demanding. By March 31, 2027, the Scams Prevention Framework will impose rigorous detection and reporting obligations on banking, telecommunications, and digital platform providers. These sectors are now required to join the Australian Financial Complaints Authority (AFCA) to ensure a coordinated response to consumer harm. The integration of these disparate industries into a unified compliance framework underscores the government’s shift toward a holistic, network-based view of risk.
A Chronology of Regulatory Pressure
The current regulatory climate is the culmination of a multi-year effort to modernize Australia’s financial integrity infrastructure. Following the release of the 2025 National Anti-Scam Centre report, policymakers accelerated the development of the Scams Prevention Framework. The timeline of key milestones includes:
- January 2025: Heightened focus on scam prevention following record-breaking financial losses.
- July 2025: Initial public consultations on Tranche 2 AML/CTF reforms.
- September 2025: Publication of the National Anti-Scam Centre’s comprehensive report on 2025 losses.
- July 1, 2026: Official commencement of Tranche 2 AML/CTF obligations, incorporating 80,000 new entities.
- September 1, 2026: The Australian Financial Crime Summit, where industry experts highlighted the "silo effect" as a primary failure point.
- March 31, 2027: Expected enforcement date for the Scams Prevention Framework, necessitating full cross-sector integration.
The fundamental disconnect, as identified by Davies, lies in the "handoff" between customer onboarding and continuous monitoring. Historically, firms have treated the KYC (Know Your Customer) process as a static, one-time event. Once a risk score is generated at the point of entry, the data is frequently relegated to an archive, disconnected from the real-time transaction monitoring systems that track customer behavior. This failure to leverage the initial due diligence during the life cycle of the customer account creates a blind spot. According to the ComplyAdvantage State of Financial Crime 2026 research, over 50% of compliance leaders are forced to manage their risk posture across eight to ten separate, disconnected systems. While 99% of these leaders acknowledge the necessity of an integrated interface, the transition remains slow due to the complexity of legacy architecture.
Beyond the Narrow Scope of FRAML
For much of the last decade, the industry focused on "FRAML"—the convergence of Fraud and Anti-Money Laundering functions. While this was a necessary evolution, it is now insufficient. Financial crime has moved beyond simple transactional irregularities. Modern illicit activity is often a byproduct of broader, more sinister criminal enterprises, including human trafficking, modern slavery, and the proliferation of illicit synthetic drugs like fentanyl. The International Labour Organization (ILO) estimates that approximately 50 million people are living in modern slavery, with the proceeds of this exploitation flowing through standard global payment networks.
Because transnational crime is estimated by Global Financial Integrity to generate between $1.6 trillion and $2.2 trillion annually, the compliance function must treat detection as a network-based exercise. When criminal organizations operate as sophisticated, cross-border supply chains, individual bank silos cannot possibly detect the patterns of money laundering that sustain them. As Davies noted during his presentation, "Financial crime is a network problem, so we have to solve this network problem with networks ourselves." This involves sharing intelligence across borders and sectors, an effort supported by bodies like FATF, FinCEN, and the Monetary Authority of Singapore (MAS).
Operational Implications and the "Overlay" Solution
The challenge for institutions is how to achieve this level of integration without the prohibitive cost and risk of a full "rip-and-replace" overhaul of their legacy technology stacks. The emerging industry standard is the deployment of an orchestration layer—a technological overlay that sits atop existing systems to unify customer identity, risk signals, and behavioral analytics.
This approach allows institutions to maintain their core banking or transactional systems while ensuring that risk data flows seamlessly between them. By creating a "single view of the customer," firms can finally quantify their risk exposure in real-time. This provides a measurable metric that can be reported to executive boards and regulatory bodies, shifting the compliance conversation from a "cost center" to a "business imperative."
Protecting the Lifetime Value of the Customer
There is a significant commercial argument for this increased vigilance. In the current digital economy, customer trust is the most valuable currency. When a financial institution effectively mitigates fraud, it is not merely fulfilling a regulatory requirement; it is actively reinforcing the customer relationship and protecting the lifetime value of the account holder. Consumers, who increasingly demand high-speed digital services, also demand, as a baseline, that those services be inherently safe.
Effective financial crime controls serve as a cornerstone of the brand promise. When an organization can demonstrate that it is a "vanguard" of safety, it engenders trust that extends beyond the individual customer and into the stability of the entire financial system. By integrating investigation outcomes back into the screening and monitoring cycles, firms create a self-improving loop where every detected instance of crime strengthens the next line of defense.
Conclusion: The Path to Future-Proofing
As the March 2027 deadline for the Scams Prevention Framework approaches, the distinction between those firms that have modernized their compliance infrastructure and those that have not will become increasingly apparent. The "point of the spear" in the fight against financial crime is no longer just the transaction monitoring analyst; it is the infrastructure that allows for the synthesis of data.
To achieve true effectiveness, firms must move away from the traditional, siloed model and toward a unified, intelligence-led architecture. By leveraging orchestration layers to connect onboarding context with ongoing monitoring, institutions can bridge the operational gap that currently allows illicit funds to move undetected. The data suggests that this is not a luxury, but a necessity; the cost of inaction, measured in billions of dollars of lost capital and the exploitation of vulnerable populations, is simply too high. Compliance, in its modern form, must be as agile and interconnected as the criminal networks it aims to disrupt. Only then can financial institutions truly claim to be effective in their role as the guardians of the global financial system.
