On March 26, 2026, the Canadian financial sector entered a new era of regulatory oversight as Bill C-12 received Royal Assent, fundamentally amending the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA). This legislative overhaul marks a decisive departure from a compliance culture focused on documentation and "check-the-box" procedural adherence toward an outcomes-based regime. Under the new framework, the Financial Transactions and Reports Analysis Centre of Canada (FINTRAC) has been granted expanded authority to penalize firms not just for missing paperwork, but for failing to ensure that their anti-money laundering (AML) programs are "reasonably designed, risk-based, and effective."
The implications of this shift are underscored by a drastic increase in financial consequences. Penalties for non-compliance have been elevated forty-fold, with cumulative fines now capped at the greater of C$20 million or 3% of a firm’s gross global revenue. For financial institutions, payment service providers, and other reporting entities, the regulatory question is no longer whether they have a policy, but whether that policy demonstrably mitigates the risk of illicit financial activity.
A Chronology of the Regulatory Pivot
The path to Bill C-12 was paved by years of scrutiny regarding the efficacy of Canada’s AML regime. Critics and international bodies, including the Financial Action Task Force (FATF), had long pointed to gaps in Canada’s ability to detect and report suspicious transactions in real-time.
- Pre-2026: FINTRAC examinations focused heavily on the existence of written policies, compliance officer designations, and proof of employee training.
- March 26, 2026: Bill C-12 receives Royal Assent, codifying the "effectiveness" standard into federal law.
- May 2026: FINTRAC publishes updated administrative monetary penalty guidance, explicitly shifting the assessment criteria to operational outcomes.
- September 2026: Industry experts, including leaders from ComplyAdvantage and Grace CSI, begin formalizing the analysis of these changes, noting that the "grace period" for adapting to these new standards is effectively over.
The Shift from Efficiency to Effectiveness
A critical distinction emerging in the post-March environment is the difference between an efficient program and an effective one. Historically, many firms focused on system efficiency—ensuring that transactions were processed quickly and that internal workflows were streamlined. However, regulators are now signaling that a system can be highly efficient at generating "garbage" output while failing to identify high-risk activity.
Claude Baksh, Co-founder and President of Grace CSI, emphasizes that the regulator’s gaze has moved beyond the surface level. "They’re no longer stopping at that evaluation of your written policies and procedures or your training," Baksh noted during a recent industry webinar. "Now they’re looking at the operational effectiveness. The test is whether your program is achieving the outcomes that it’s expected to achieve based on your institution’s assessed risk profile and risk exposures."
This shift has created a significant challenge for firms struggling with alert backlogs. Under the new regime, a system that generates a massive volume of alerts which a human team cannot process is, by definition, ineffective. FINTRAC is now scrutinizing the ratio of alerts to filed Suspicious Transaction Reports (STRs). If a firm’s backlog prevents it from reviewing and reporting, the firm is failing the test of operational effectiveness.
Data-Driven Enforcement and Peer Benchmarking
FINTRAC’s new methodology relies heavily on cross-entity data. By benchmarking firms against their peers—comparing companies with similar product sets, customer demographics, and geographic exposure—the regulator can identify outliers. If an institution reports significantly fewer STRs than a comparable firm in the same sector, that statistical anomaly alone is now sufficient grounds for a formal examination.
This benchmarking approach serves as a powerful deterrent against passive compliance. The data-driven nature of these assessments means that reporting output acts as direct, objective evidence of a program’s health. As firms integrate more advanced analytical tools, the expectation is that they will not only detect more risk but will be able to demonstrate why certain transactions were flagged and others were not.
The Structural Failure: Legacy Fragmentation
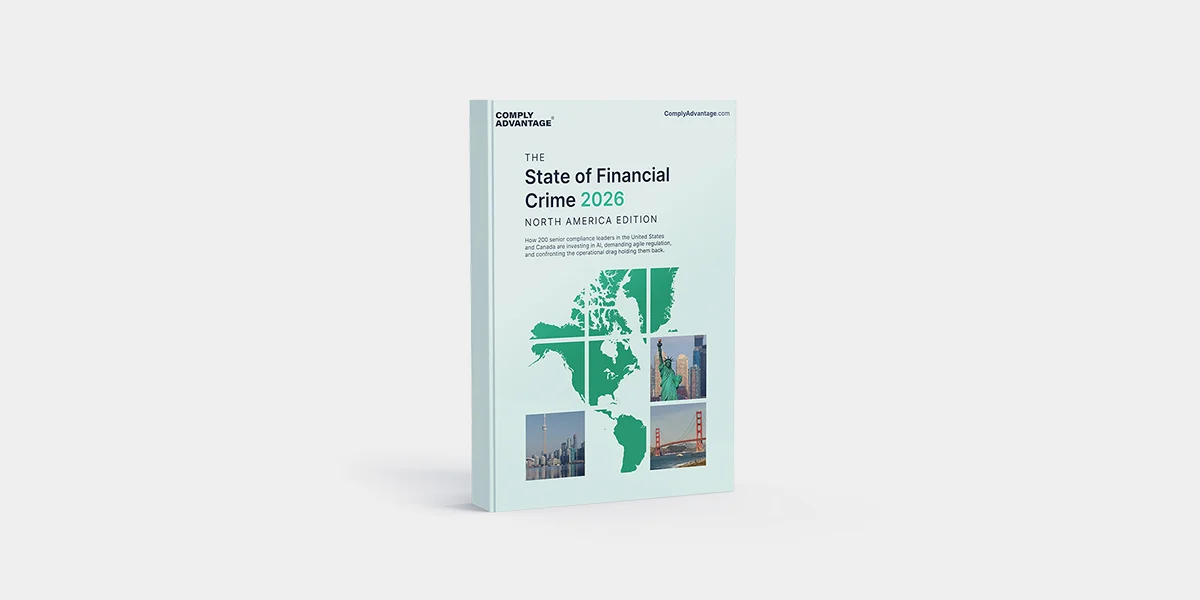
Research presented in the State of Financial Crime 2026 report highlights a significant barrier to this new standard: technological fragmentation. Roughly 35% of Canadian firms report limitations in their ability to screen customers against sanctions and watchlists, often juggling an average of more than six separate, disconnected screening solutions.
These legacy systems frequently suffer from three primary flaws:
- Data Silos: Information is trapped in departmental pockets, preventing a holistic view of a customer’s risk profile.
- Static Rule Engines: Systems are unable to adapt to real-time payment volumes or the rapid evolution of modern financial crime typologies.
- Lack of Tailoring: Many firms rely on "off-the-shelf" rules that do not reflect their specific risk appetite, resulting in excessive noise that masks genuine threats.
Andrew Davies, Global Head of FCC Strategy at ComplyAdvantage, notes that the speed of modern finance necessitates a change in how we view compliance technology. "If we want to follow the money that’s moving instantaneously, either domestically in Canada or around the world, we need to have data and technology that can react at the speed of these financial services," Davies stated.
Demonstrating Compliance: The Requirement for Explainability
To survive a FINTRAC audit under the new rules, firms must move toward "explainable compliance." This requires more than just automated logs; it demands a clear, human-readable audit trail that justifies every automated decision.
Key requirements for firms include:
- Documented Risk Assessments: A transparent link between the firm’s identified risk profile and the specific detection scenarios implemented in production.
- Threshold Management: Clear, logged explanations of why specific thresholds were chosen and how they have been adjusted over time as threat environments shifted.
- Model Validation: Maintaining historical versions of detection models to ensure that past decisions can be re-run and analyzed by examiners.
- Human-in-the-loop Processes: Ensuring that all automated systems are supported by expert analysis, with detailed notes attached to files that explain the reasoning behind an STR filing or a decision not to file.
"You’ve got to have notes on your files," says Baksh. "You can’t just have automated decisions being made without that plain language explanation that’s factual, that you can defend."
The Strategic Business Case
While the cost of upgrading AML infrastructure is substantial, industry leaders argue that the investment offers benefits beyond regulatory safety. By refining risk-based screening, firms can reduce false positives, which in turn accelerates customer onboarding and improves the user experience.
Furthermore, the data collected for AML purposes—behavioral patterns, transaction velocity, and geographic activity—can be repurposed to provide business intelligence, fraud detection, and market segmentation. By viewing AML as a data asset rather than a regulatory burden, firms can better align their compliance spending with broader organizational goals.
Broader Implications for the Canadian Financial Sector
The implementation of Bill C-12 and the associated FINTRAC guidance represents a maturation of the Canadian regulatory environment. As the country aligns more closely with global best practices, the burden on financial institutions has reached an inflection point. The "business as usual" approach—characterized by fragmented systems, backlogs, and purely administrative oversight—is no longer viable.
Moving forward, the institutions that will succeed are those that embrace an integrated, evidence-based approach to compliance. By fostering a culture where data is consistent, models are explainable, and the link between risk assessment and reporting is transparent, firms can navigate the new, higher-stakes landscape. The message from the regulator is clear: in an era of instantaneous finance, the only acceptable compliance program is one that works in real-time, effectively, and with the full backing of institutional data.
For the Canadian market, the next few years will be defined by this transition. The penalty for failure is no longer just a reputational risk or a minor fine; it is an existential threat to the bottom line, reinforcing the reality that in the modern financial system, there is no substitute for objective, proven effectiveness.