On March 26, 2026, the legislative landscape for anti-money laundering (AML) and counter-terrorist financing (CTF) in Canada underwent a seismic shift as Bill C-12 received Royal Assent. This pivotal legislation fundamentally overhauled the Proceeds of Crime (Money Laundering) and Terrorist Financing Act (PCMLTFA), moving the regulatory goalposts from simple procedural compliance to a rigorous, results-oriented framework. For Canadian financial institutions and reporting entities, the era of "check-the-box" compliance has effectively ended, replaced by an urgent mandate to prove that AML programs are not merely present, but demonstrably effective.
The Regulatory Evolution: From Documentation to Outcome
The core change introduced by Bill C-12 centers on the requirement that compliance programs must be "reasonably designed, risk-based and effective." While previous iterations of the PCMLTFA focused heavily on the existence of written policies, training logs, and basic reporting structures, the modern FINTRAC (Financial Transactions and Reports Analysis Centre of Canada) assessment model looks directly at operational output.
The legislative shift was codified in updated administrative monetary penalty guidance published by FINTRAC in May 2026. This guidance explicitly signals that the regulator is no longer satisfied with reviewing the architecture of a compliance program; they are now interrogating its mechanical output. If a firm’s internal controls are theoretically sound but fail to identify and report suspicious activities that peers with similar risk profiles are capturing, the program is deemed ineffective.
The financial stakes for failure have escalated dramatically. Penalties for non-compliance have increased forty-fold, with potential fines reaching the greater of C$20 million or 3% of a firm’s gross global revenue. This ceiling represents a significant deterrent, intended to force board-level attention toward compliance infrastructure that had, in some sectors, suffered from underinvestment.
Chronology of the Shift
The transformation of the Canadian regulatory environment did not happen in a vacuum. It was the culmination of years of pressure to align Canadian standards with international best practices set by the Financial Action Task Force (FATF).
- Pre-2026: A period characterized by static rule-based monitoring and a focus on administrative documentation.
- March 26, 2026: Bill C-12 receives Royal Assent, formalizing the requirement for "effective" compliance programs and drastically increasing potential monetary penalties.
- May 2026: FINTRAC releases updated administrative monetary penalty guidance, shifting the focus of examinations toward operational effectiveness and outcomes.
- September 2026: Industry experts and stakeholders begin to analyze the first six months of enforcement, noting that FINTRAC has begun utilizing cross-entity benchmarking to identify under-reporting outliers.
Benchmarking and the Data-Driven Regulator
A key feature of the new enforcement regime is FINTRAC’s use of advanced data analytics to benchmark firms against their peers. By aggregating data across sectors, the regulator can establish a baseline for what "normal" suspicious transaction report (STR) volume looks like for institutions with similar product offerings and customer bases.
For institutions that find themselves filing significantly fewer STRs than their competitors, the burden of proof has effectively shifted. Such firms are now primary candidates for intensive examinations. In this context, an entity’s reporting volume is no longer just a regulatory filing; it is the primary evidence used by regulators to assess whether a firm’s risk-detection engines are functioning correctly.
Claude Baksh, Co-founder and President of Grace CSI, notes that the distinction between efficiency and effectiveness is now a point of high-stakes scrutiny. "You can have an efficient system that delivers garbage versus an effective system," Baksh explains. An "efficient" system that is overwhelmed by false positives—and therefore leaves a massive backlog of unreviewed alerts—is now considered a failure of design. A backlog is no longer an excuse for delayed reporting; it is, in the eyes of the regulator, an indicator of an inadequate system that lacks the scalability to handle real-time financial flows.
The Technological Hurdle: Legacy Systems vs. Modern Threats
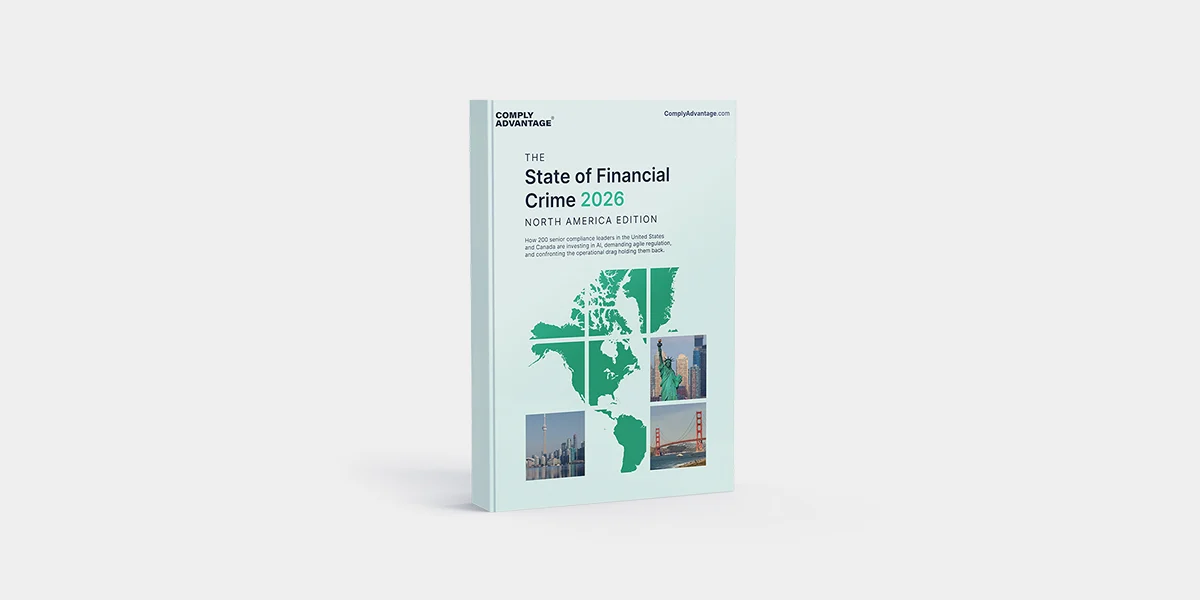
Research conducted for the State of Financial Crime 2026, North America edition, reveals a concerning technological gap: approximately 35% of Canadian firms struggle with fundamental limitations in screening customers against sanctions and watchlists. Many of these firms are relying on fragmented, legacy platforms that resist integration and lack the flexibility to adapt to evolving criminal typologies.
These legacy systems often operate on rigid, static rule engines that cannot keep pace with the speed of modern digital transactions. When firms apply "off-the-shelf" rules without tailoring them to their specific risk environment, the result is excessive noise. This noise obscures genuine threats, leading to the very backlogs that regulators now cite as evidence of an ineffective program.
Andrew Davies, Global Head of FCC Strategy at ComplyAdvantage, emphasizes that the solution requires a fundamental rethinking of data architecture. "If we want to follow the money that’s moving instantaneously, either domestically in Canada or around the world, we need to have data and technology that can react at the speed of these financial services," Davies states. This requires a move toward unified data ingestion and consistent definitions, ensuring that the firm has a singular, transparent view of risk across all business lines.
Establishing the "Explainability" Standard
For compliance teams, the new mandate requires a high degree of "explainability." Auditors now demand to see the logic behind every automated decision. Firms must be prepared to provide:
- Documented Risk Assessments: A clear, written rationale that links specific detection scenarios to the firm’s assessed risk profile.
- Threshold Management: Detailed logs that track why detection thresholds were adjusted, when they were adjusted, and how those adjustments align with changes in the threat landscape.
- End-to-End STR Trails: A granular view of how high-priority alerts are managed, with clear, plain-language notes justifying why an alert did or did not result in a formal filing.
This is not merely an IT task; it is a governance requirement. The ability to retain historical model versions and re-run them to demonstrate the basis for a past decision is now standard expectation. Without this, firms cannot defend their decision-making processes during an examination.
Broader Implications and Strategic Alignment
The implications of Bill C-12 extend beyond the compliance department. Because the regulatory focus is now on the "effectiveness" of data-driven systems, compliance is becoming increasingly linked to broader business objectives. Firms that can leverage their AML infrastructure for fraud detection, customer behavior analysis, and market segmentation are finding that the investment required to satisfy FINTRAC also yields significant business intelligence.
However, the path to compliance remains difficult for firms trapped in silos. The most successful organizations are those that have begun to break down the walls between their IT, risk, and business units. By aligning AML initiatives with the broader corporate strategy, firms can secure the budget and executive buy-in necessary to move beyond legacy limitations.
As the industry moves into the latter half of 2026, the divide between firms that have adapted to the new effectiveness mandate and those that are still attempting to patch legacy systems will likely widen. The "effectiveness" test is not a one-time audit but an ongoing operational standard. Firms that treat their data as a strategic asset—and their compliance program as a dynamic, evolving capability—will be the best positioned to navigate the heightened scrutiny of the post-C-12 era.
In conclusion, the legislative intent behind Bill C-12 is clear: to ensure that Canada’s financial system is a hard target for illicit actors. By demanding that institutions not only have systems in place but can also prove those systems work, the regulator has effectively mandated a new level of professionalization in the Canadian financial sector. For the firms that succeed in this transition, the reward is not just regulatory safety, but a more resilient, data-informed, and competitive business.