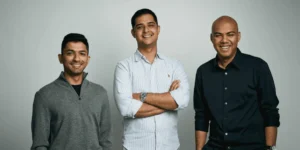
The rapid adoption of artificial intelligence across corporate enterprises has introduced unprecedented operational efficiencies, but it has simultaneously unveiled a sprawling and largely unmonitored attack surface. As organizations increasingly transition from passive generative AI chat interfaces to autonomous agents capable of executing complex, multi-step workflows, the security paradigm is shifting beneath the feet of Chief Information Security Officers (CISOs). Into this volatile landscape steps Air, a cybersecurity startup founded by Israel Defense Forces Unit 8200 alumni Yair Saban and Niv Hoffman. Backed by venture capital heavyweights including Sequoia Capital—which recently doubled down on the enterprise by leading the company’s Series A financing following an initial seed round—Air is positioning itself as the definitive system of record for securing the autonomous agent supply chain.
The Genesis and Pedigree of an Elite Founding Team
The foundation of Air is rooted in the formidable pedigree of Israel’s elite cyber intelligence corps, Unit 8200. Long before Saban and Hoffman incorporated a company, established a formal brand identity, or finalized a commercial product, their reputations preceded them within the close-knit Israeli cybersecurity ecosystem. References gathered from former commanders painted a picture of exceptional technical aptitude and leadership capacity. Notably, a former commander of Unit 8200 remarked that Saban was the only individual encountered during their service possessing all the requisite qualities to command the unit itself—an endorsement of the highest order in the region’s hyper-competitive tech sector. Co-founder Niv Hoffman is recognized as a technical outlier who previously spearheaded Unit 8200’s premier vulnerability research department, cultivating an extensive network of elite technical talent in the process.
The velocity with which the founding team operates became evident immediately upon the conclusion of their military service. Upon finishing his active duty on a Thursday, Saban reportedly shook hands with investors on a seed investment agreement that very Saturday. This rapid execution tempo set the tone for the company’s early product development cycle, which prioritized aggressive vulnerability research and public demonstrations over quiet incubation.
Exposing the Flaws: From MOAK to SkillJacking
Before pivoting to comprehensive defensive architecture, the founders sought to jolt the broader cybersecurity industry into recognizing the asymmetric leverage that artificial intelligence affords modern attackers. To achieve this, Saban and Hoffman developed MOAK—an acronym playfully referring to the "Mother of All KEVs" (Known Exploited Vulnerabilities). MOAK is an agentic workflow engineered to autonomously generate working exploits for freshly published vulnerabilities without human intervention.
In a public demonstration of the framework’s capabilities, MOAK successfully exploited a React vulnerability in a mere 21 minutes. By contrast, the industry average for an enterprise to formulate, test, and deploy a corresponding security patch is approximately six days. By releasing MOAK publicly, the founders intended to sound an alarm: defensive tooling and patch management cycles were dangerously lagging behind the speed at which AI-driven offensive actors could weaponize fresh CVEs.
This research trajectory continued with the publication of the "Story of Skills" project. Air demonstrated that a deliberately malicious AI skill—written by researchers to test marketplace hygiene—could successfully bypass automated and manual security scanners. Distributed through trusted marketplaces and social media channels, the rogue skill reached more than 26,000 active AI agents while every standard scanner cleared it as benign.
The security implications were further compounded by the release of Air’s "SkillJacking" research. The study revealed that 925 live, publicly available skills were improperly configured, pulling their vital dependencies and operational prompts from dead, unregistered Uniform Resource Locators (URLs). Air systematically registered those abandoned links, effectively gaining administrative control over approximately 134,000 enterprise agents that had installed the compromised skills. Every public vulnerability scanner tested against these flaws failed to detect the anomalies entirely.
Coinciding with these disclosures, Saban and Hoffman released ScanAir, an OWASP-aligned security scanner designed specifically to audit agentic skills. This operational rhythm—identifying a systemic architectural flaw, empirically proving it through rigorous testing, publicizing the findings for industry awareness, and immediately shipping a remediation tool—has become the defining signature of Air’s market entry strategy.
The Agentic Supply Chain Crisis
To understand the necessity of Air’s product suite, industry analysts draw parallels to the evolution of traditional software development. Decades ago, when software engineers transitioned from writing monolithic codebases to importing third-party packages, modern software architecture acquired a complex supply chain. It subsequently took over twenty years—punctuated by high-profile, systemic security crises such as Log4j and the SolarWinds supply chain compromise—for the industry to establish robust inspection machinery for incoming code.
Autonomous AI agents face an identical structural vulnerability, but with a critical compounding factor: an agent’s supply chain is dynamically assembled at runtime, and in many enterprise environments, it goes entirely uninspected. A modern corporate AI agent consumes a diverse array of modular components, including specialized skills, plugins, Model Context Protocol (MCP) servers, sub-agents, hooks, custom commands, and behavioral rules.
Crucially, each of these components executes with the agent’s own high-level permissions, directly within a user’s local or cloud environment, with unhindered access to sensitive corporate data. In most current enterprise deployments, these powerful add-ons are installed by end-users with the casual negligence typically reserved for downloading minor browser extensions.
A Comprehensive Three-Tiered Defense Architecture
To address the full lifecycle of agent add-ons and secure this fragile runtime supply chain, Air has developed an integrated, three-product portfolio. Industry experts have likened the architecture to a comprehensive home security system, where every potential entry point is accounted for and managed centrally.
-
Air Filter (The Locks and Childproofing): Operating at the ingestion phase, Air Filter vets every prospective add-on before an agent is permitted to consume or execute it. The system employs a multi-layered approach combining static code analysis, deep dependency checking, and isolated sandbox detonation. If a malicious or non-compliant add-on is detected, Air Filter intercepts the installation in real time and automatically suggests secure, verified alternatives.
-
Air Defend (The Cameras and Monitoring): Once agents are actively running in production, Air Defend takes over by continuously monitoring their runtime behavior. It provides enterprise security operations (SecOps) teams with advanced detection, alerting, and incident response capabilities specifically tailored to autonomous agent activity, flagging anomalous execution paths or unauthorized data access attempts.
-
Air Control (The Master Control Panel): Handling overarching posture management and governance policies, Air Control maintains a definitive inventory of every active agent within the organization, mapping precisely what systems and data resources they are authorized to touch. Crucially, if a vulnerability is discovered in a widely deployed skill, Air Control allows administrators to instantly revoke that specific component across thousands of disparate agents simultaneously.
Implications for the Enterprise CISO
As corporate boardrooms push for deeper automation and hand over genuine operational authority to AI agents operating across core business systems, Chief Information Security Officers face an uncomfortable reckoning. When queried by executive leadership regarding the security posture of their autonomous deployments, few CISOs currently possess complete, defensible answers to foundational questions: What code is our agent actually running? Where did those components originate? Who vetted them before deployment?
Air is actively engineering the operational infrastructure designed to provide those definitive answers. By consolidating top-tier talent from Israel’s premier technological units and maintaining an aggressive posture toward vulnerability research and remediation, the company is attempting to establish the definitive system of record for the agentic era. As enterprise AI transitions from experimental novelty to core economic engine, the ability to secure the runtime supply chain will dictate which organizations safely scale their automation—and which fall victim to the next generation of automated exploits.