The rapid integration of autonomous AI agents into enterprise workflows has created a significant new vector for security vulnerabilities, prompting a surge in demand for specialized risk management solutions throughout the third quarter of 2026. As these agents gain the autonomy to execute complex tasks—from managing supply chains to initiating financial transactions—the perimeter of the modern enterprise has effectively shifted from static networks to dynamic, AI-driven decision engines. According to recent market analysis, the imperative to govern these agents is no longer an experimental project but a core mandate for Chief Information Security Officers (CISOs) worldwide.
The Evolution of the AI Threat Landscape
The shift in enterprise security strategy is rooted in the transition from traditional, rule-based automation to large-scale, generative AI agent systems. In previous years, security teams focused primarily on securing endpoints, cloud storage, and identity access management. However, as of late 2026, the focus has pivoted toward "Agentic Governance."
The challenge lies in the autonomy granted to these models. Unlike legacy software, which performs predefined scripts, AI agents are designed to reason, interact with third-party APIs, and retrieve data from diverse enterprise silos. This capability creates "shadow AI" risks, where agents may inadvertently expose sensitive data or perform unauthorized actions due to prompt injection attacks or hallucinations. As a result, the market for AI agent security has transitioned from a niche concern into a robust sector, with data from industry trackers indicating that over 160 private companies are now actively developing solutions to mitigate these specific risks.
Chronology of the Shift: From Prototype to Production
The timeline for this transition accelerated rapidly in early 2026. By the first quarter, early-adopter enterprises began reporting incidents of "agent drift," where AI systems were found to be accessing internal repositories beyond their intended scope. By May 2026, major cybersecurity conferences were dominated by discussions regarding the "trust gap" in AI workflows.
Following this, the summer of 2026 saw a wave of strategic acquisitions as established cybersecurity vendors sought to integrate AI-native security protocols into their existing suites. By September 2026, the market entered a phase of maturity, characterized by the emergence of pure-play startups that focus exclusively on securing the "reasoning layer" of AI applications. This progression reflects a classic technological adoption cycle, where initial enthusiasm for functionality is tempered by the reality of operational risk, ultimately leading to the professionalization of the security infrastructure surrounding that technology.
Professional Pedigree: The Veteran Pivot
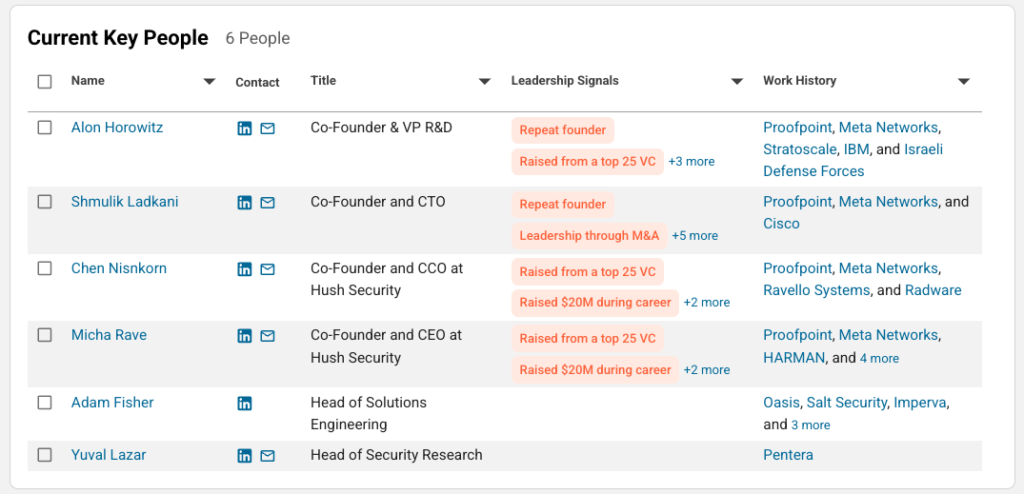
A notable trend observed throughout the recent funding cycles is the migration of veteran cybersecurity leadership into the AI agent security space. The current crop of founders is not composed of industry newcomers, but rather seasoned professionals who cut their teeth in zero-trust architecture, identity management, and network security.
For instance, the leadership behind companies like Hush Security, Geordie AI, and Keycard consists of individuals who previously architected the very infrastructure that current enterprises rely on for basic security. Micha Rave, for example, brings the experience of building and exiting Meta Networks to the challenges of AI risk. Similarly, the movement of talent from companies like Darktrace and Auth0 into the agent security domain suggests that the industry is applying the "tried and true" playbooks of identity and network protection to the volatile world of LLM-based agents.
This trend provides institutional investors with a level of comfort; these founders are not attempting to solve a new problem with unproven methodologies, but are instead adapting battle-tested frameworks to the specific behavioral idiosyncrasies of AI agents. The industry consensus is that while the threat model is novel, the principles of least privilege, auditability, and anomaly detection remain the gold standard for defense.
Market Traction and the Funding Pipeline
The investment landscape for 2026 highlights a clear differentiation between companies that are merely "AI-enabled" and those that are "AI-native." Keycard, which secured a significant Series A round in October 2025, serves as a bellwether for the sector. Its aggressive expansion strategy—evidenced by the acquisition of Runebook for MCP-powered agent infrastructure and Anchor.dev for autonomous coding capabilities—signals a move toward consolidating the agent security stack.
Market data suggests that other emerging players, such as Certiv and Tynapse, are approaching critical funding windows in the final quarter of 2026. These companies are positioning themselves as the "control planes" for the next generation of enterprise AI, aiming to provide a unified interface for policy enforcement across various agent architectures. Analysts note that these upcoming funding rounds will likely be driven by the need to scale operations as enterprises move from pilot-phase AI deployments to full-scale, mission-critical operations.
Broader Implications for the Enterprise
The implications of this shift are profound for the broader digital economy. As organizations increasingly delegate decision-making authority to AI agents, the ability to monitor, log, and audit these decisions becomes a regulatory requirement. In sectors like finance, healthcare, and critical infrastructure, the failure to secure AI agents could lead to catastrophic operational disruption or severe compliance penalties.
Furthermore, the rise of the "agent-to-agent" economy—where AI systems negotiate and interact with each other without human intervention—will necessitate an even more robust layer of security. We are entering an era where human-centric security controls are no longer sufficient. The security architecture of 2027 and beyond will need to operate at the speed of machine cognition, utilizing real-time, AI-driven defense mechanisms to counter AI-driven threats.
Contextualizing Insurtech in the AI Era
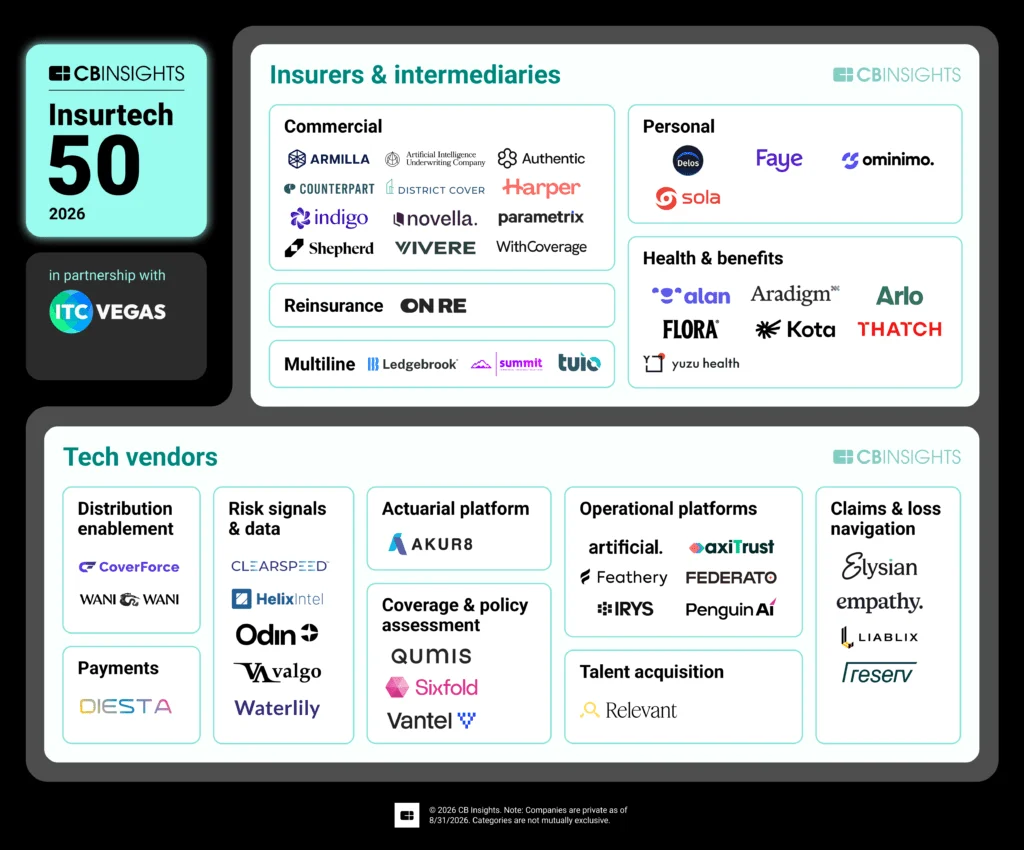
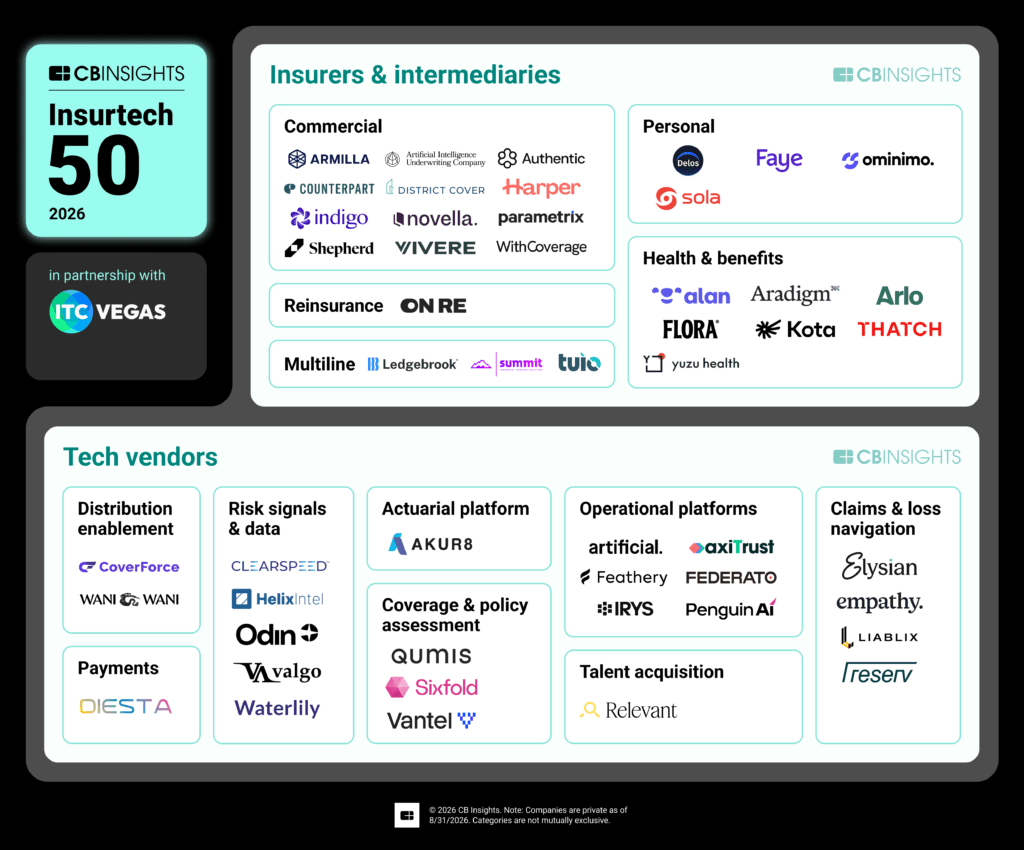
Parallel to the rise of AI security, the insurtech sector is experiencing its own transformation. The 2026 Insurtech 50 list, released recently in partnership with ITC Vegas, highlights how data analytics and AI are being leveraged to redefine risk assessment. Just as AI agents require new security paradigms, the insurance industry is being forced to adapt to the risks introduced by AI itself. Companies that can effectively model the risks associated with autonomous AI failure are likely to become the next generation of industry leaders. The intersection of these two sectors—AI security and insurtech—presents a massive opportunity for innovation, as enterprises seek to offload the residual risks that technical security measures cannot fully mitigate.
Conclusion: Preparing for the Agentic Enterprise
As the year draws to a close, it is evident that the "Wild West" phase of enterprise AI adoption is concluding. The pressure to secure AI agents has become a defining characteristic of the 2026 tech landscape. Enterprises that prioritize the implementation of rigorous governance, observability, and security frameworks for their AI agents will be better positioned to reap the benefits of increased productivity without compromising their digital integrity.
The next twelve months will likely be defined by a "flight to quality," where enterprises consolidate their AI toolkits around vendors that offer verifiable security, transparent audit trails, and, most importantly, the ability to adapt to the rapidly changing tactics of adversaries. For the security professional, the challenge of 2026 is clear: as agents become more intelligent and autonomous, the security perimeter must evolve from a wall to a neural network, capable of understanding context, intent, and impact in real-time. The era of the agentic enterprise has arrived, and with it, the urgent necessity to secure the logic that drives the modern business.