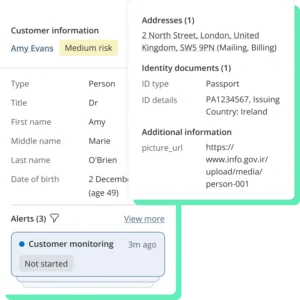
Financial products used to travel through predictable, contained channels, branches, telephone banking, card networks and traditional payment rails, all of which could be monitored and controlled with relative ease. That world has largely disappeared. The contemporary financial ecosystem is characterized by an intricate web of digital touchpoints, instant payment networks, and cross-border integrations that challenge the very foundations of traditional banking supervision. According to a recent analysis published by Arctic Intelligence, digital onboarding, mobile-first platforms, instant transfers, API-driven services, embedded finance, and crypto-enabled channels have fundamentally reshaped how customers engage with banks and FinTechs. In doing so, they have birthed a sophisticated, highly volatile category of delivery channel risk that conventional compliance frameworks are ill-equipped to handle.
The Obsolescence of Binary Risk Classifications
For decades, financial crime risk assessments (FCRAs) relied on simplistic, binary categorizations to evaluate customer interactions. Institutions routinely divided their operations into "face-to-face" versus "non-face-to-face" channels, assuming that physical presence equated to lower risk while remote interactions required heightened scrutiny.
However, this binary framework has become dangerously obsolete. Channels have quietly transitioned from passive pathways into some of the primary drivers of financial crime exposure. They actively shape customer experiences, influence transaction behaviors, and dictate an institution’s visibility into underlying risks. Despite this paradigm shift, many financial institutions continue to rely on legacy classification models. These outdated systems fail to capture the nuanced realities of modern digital engagement, leaving blind spots that illicit actors readily exploit.
The rapid democratization of financial services through mobile applications and web portals offers undeniable benefits in terms of speed, scale, and financial inclusion. Yet, those exact attributes serve as double-edged swords. Instant onboarding accelerates legitimate business growth, but it can equally fast-track fraudulent accounts, money laundering schemes, terrorist financing, and proliferation financing if proper safeguards are bypassed or inadequate. Frictionless mobile experiences designed to delight genuine consumers inadvertently provide malicious actors with the ideal cover to blend in unnoticed.
The Complex Web of Intermediaries and Banking-as-a-Service
Adding unprecedented layers of complexity to the compliance landscape is the explosive growth of third-party intermediaries. The modern financial delivery chain rarely relies on a single institution from end to end. Instead, it frequently incorporates a diverse array of FinTech partners, payment facilitators, Banking-as-a-Service (BaaS) providers, digital wallets, and decentralized or centralized crypto exchanges.
Each entity within this collaborative network carries its own unique risk profile, technological architecture, and internal control environment. Despite this decentralization, regulatory bodies across major jurisdictions maintain that the licensed, regulated financial institution remains ultimately accountable for compliance failures throughout the entire delivery chain.
Market data indicates that a significant percentage of regulated entities continue to underestimate the compounded risk introduced by these extended intermediary networks. When a product is built by one firm, hosted by a BaaS provider, distributed through a FinTech app, and funded via a digital wallet, the resulting interdependencies create an intricate mosaic of operational and regulatory exposure that simple, isolated channel labels simply cannot capture.

Behavioral Shifts, Velocity Risk, and Rapid Channel-Switching
Customer transaction habits have evolved in direct alignment with these new delivery channels. The introduction of real-time payments across global financial market infrastructures has drastically heightened velocity risk. Funds can now move across international borders in fractions of a second, leaving compliance teams with vanishingly small windows to intercept suspicious transactions.
Concurrently, the proliferation of digital wallets has intensified anonymity concerns, while embedded finance has effectively blurred the lines separating traditional merchants, digital platforms, and everyday consumers. Transaction monitoring systems that were originally architected for slower, batch-processed, and predictable transaction patterns are visibly struggling to keep pace. They frequently fail to detect velocity spikes, complex cross-platform financial flows, and rapid channel-switching behaviors. Risk assessments that ignore these dynamic realities risk severely underestimating an institution’s true financial crime exposure.
Crucially, the chosen delivery channel now actively dictates both inherent and residual risk. It establishes how reliably an individual or corporate identity can be verified at inception and dictates how quickly transaction anomalies can be identified and remediated. A high-grade, complex financial product delivered through a tightly controlled, highly monitored channel can often be managed effectively. Conversely, a seemingly low-risk product pushed through a poorly controlled, highly fragmented channel can quickly escalate into a major regulatory liability. In the modern era, the delivery channel no longer merely facilitates the customer relationship—it fundamentally defines it.
Industry Reactions and Regulatory Implications
As financial services grow increasingly digital and interconnected, risk management experts and regulatory consultants are urging a radical overhaul of compliance strategies. Industry stakeholders emphasize that institutions must move far beyond traditional channel classifications. They must instead incorporate granular data regarding customer behavior, device intelligence, third-party intermediation, and transaction velocity into their core risk models.
Financial crime compliance officers note that regulatory expectations are shifting in tandem with technological advancements. Regulators in key markets are no longer satisfied with static risk assessments that treat channels as background variables. Instead, supervisory authorities are demanding dynamic, data-driven frameworks that continuously evaluate how digital products are delivered, monitored, and controlled.
Strategic Outlook and Future Resilience
The trajectory of financial technology suggests that delivery channels will continue to evolve at a pace that far outstrips the traditional regulatory frameworks designed to contain them. Emerging paradigms—such as decentralized finance (DeFi) integrations, hyper-personalized AI-driven financial agents, and instantaneous cross-border stablecoin settlements—will only deepen the complexity of the digital delivery challenge.
Institutions that proactively modernize their financial crime risk assessments to account for these multifaceted dynamics will find themselves vastly better positioned to manage regulatory exposure. By transitioning from rigid checklists to holistic, behavior-based channel oversight, banks and FinTechs can preserve operational agility while safeguarding the integrity of the global financial system against sophisticated financial crime.